SecureWorld conferences blend world-class keynotes, breakout sessions, small group discussions, and opportunities to earn CPE credits.
-
How Winnebago Industries Turns Security Awareness into a Shared Responsibility
 Information Security Analyst, Winnebago Industries
 Sr. Security Engineer, Winnebago Industries
 VP of Information Security, Winnebago Industries
-
 CISO, Cengage
 Director, Cybersecurity, Anderson Corporation
 CISO, Metropolitan Airports Commission
 Sr. Director, IT Infrastructure & Cybersecurity, Restaurant Technologies
 Open Sessions
 Conference Pass
 SecureWorld Plus
 VIP / Exclusive
- Wednesday, November 18, 20269:00 am[PLUS Course] Securing & Enabling AI: Transform Chaos into Competitive Advantage
 Registration Level:
- SecureWorld Plus
9:00 am - 3:00 pmYour CEO just asked about AI security. Do you have a clear answer?While you’re counting vulnerabilities, your competitors are deploying AI at scale.While security teams are still cataloging vulnerabilities, business units are deploying AI at scale. Marketing is using generative AI for campaigns. Sales is rolling out AI SDRs. Customer service is automating with chatbots.Every Monday, another department launches an AI tool. Marketing uses ChatGPT for campaigns. Sales deploys AI Sales Development Reps. Customer service automates with chatbots. And your cybersecurity team? Still writing policies nobody reads.In this interactive workshop, learn you how to secure AI while accelerating innovation—not blocking it. Transform from AI Firefighter to Strategic Business Enabler, with a 90-day roadmap for secure AI deployment in your organization.What You’ll Master-
The AIR-MAP Methodology™ — Your proven 90-day roadmap from AI chaos to governance
-
Executive Translation — Turn technical AI risks into boardroom language
-
NIST AI RMF Implementation — Practical application, not theory
-
The $12M Question — Secure against deepfake fraud and AI-enabled attacks
-
Shadow AI Discovery — Find and govern the AI already in your organization
-
Business-First Security — Protect value, not just systems
Who Should AttendIdeal for:-
CISOs facing board questions about AI
-
Information Security Directors enabling digital transformation
-
IT VPs without dedicated security teams
-
Cybersecurity Consultants serving enterprise clients
-
Risk Managers governing AI initiatives
-
Aspiring decision makers and those reporting to one
Not designed for:-
Developers wanting to code AI models
-
Analysts seeking technical certifications
-
Anyone looking for hands-on hacking labs
What This Workshop Is (and Isn’t)This workshop is NOT about:-
Prompt injection techniques
-
Model architecture security
-
Technical vulnerability scanning
-
Writing 200-page policies
This workshop IS about:-
Speaking profit-and-loss to executives
-
Enabling your AI transformations
-
Building cybersecurity into AI from day one
-
Becoming the trusted AI advisor
What You’ll Leave With1. The Complete AIR-MAP Toolkit-
90-day implementation roadmap
-
Discovery templates and workflows
-
Risk scoring calculators
-
Executive presentation templates
2. Ready-to-Deploy Governance Assets-
AI Acceptable Use Policy (customize in minutes)
-
Vendor assessment questionnaires
-
Incident Response playbooks
3. A 30-Minute Strategy SessionA complimentary private consultation to apply AIR-MAP directly to your organization’s AI strategy and risk posture. - Thursday, November 19, 20267:30 amRegistration openRegistration Level:
- Open Sessions
7:30 am - 4:15 pmLocation / Room: Registration DeskCome to the Registration desk in the lobby to check-in and get your badge. SecureWorld staff will be available throughout the day if you have any questions.
8:00 amNetworking Hall openRegistration Level:- Open Sessions
8:00 am - 4:45 pmLocation / Room: Networking HallYour opportunity to visit our solution vendor partners, whose sponsorship makes SecureWorld possible, as well as association chapters! Booths have staff ready to answer your questions. Look for participating Dash For Prizes sponsors to be entered to win prizes.
Also, look for “Cyber Connect” discussions on select topics and join the conversation.
8:00 amAdvisory Council Roundtable Breakfast (VIP / Invite only)Registration Level:- VIP / Exclusive
8:00 am - 8:45 amModerated discussion for SecureWorld Advisory Council members. By invite only.
8:00 amInfraGard Minnesota Members Alliance MeetingOne Click from Water: Live Exploit Chains in Unauthenticated SCADA Registration Level:
- Open Sessions
8:00 am - 8:45 amCome join this guest speaker presentation of the InfraGard Minnesota Members Alliance.
One click during a routine water-treatment pen test, and, boom! now looking at a live SCADA control panel—pumps spinning, valves indicating, chemical mixing—running on the public internet with no authentication. It relayed any backend command an attacker wanted to send: read alarms, override setpoints, dump the entire configuration including encrypted operator credentials. The vendor’s response when this was disclosed? “Just enable authentication.” The fix wasn’t a fix.
Three years later, that same backdoor still ships, still hits hundreds of internet-exposed deployments, and now there’s a new development: re-analyzation of the entire codebase in an afternoon found 41 more vulnerabilities, including five end-to-end attack chains the original engagement never had time to enumerate. One of those chains is reverse-engineering the vendor’s “proprietary encryption,” which turns out to be a hardcoded key the same in every shipped binary!
This presentation shows five working attack chains for this (live, running) software package and does an in-depth walkthrough of one, showcasing the exploitation process. By the end, attendees will understand why any security program’s biggest exposure isn’t the code the team wrote; it’s the vendor software running inside the perimeter.
8:00 amSimple Daily Habits to Strengthen Your Security PostureRegistration Level:- Open Sessions
8:00 am - 8:45 amSession details to come.
8:45 amNetworking BreakRegistration Level:- Open Sessions
8:45 am - 9:00 amLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
9:00 am[Opening Keynote] Behavioral Threat Intelligence: Profiling Cyber Attackers Cyber Behavioral Profiler, FBI (Ret.) and Modus CyberandiRegistration Level:
- Open Sessions
9:00 am - 9:45 amLocation / Room: Keynote TheaterThreat Intelligence is more than just TTPS, IOCs and technical data—cyber attackers are individuals with motivations, behavioral patterns, emotions and cognitive processes that shape their attacks. In this session, we will explore Behavioral Threat Intelligence (BTI) as a critical complement to traditional cyber threat intelligence. By applying cyber behavioral profiling, we can uncover attacker mindsets, predict threat evolution, and enhance defense strategies. Learn how profiling cyber adversaries—from nation-state actors to cybercriminals—can provide actionable intelligence to strengthen your security posture.9:45 amNetworking BreakRegistration Level:- Open Sessions
9:45 am - 10:15 amLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
10:15 am[Panel] Bridging the Gap: The Role of the BISO in Modern Cybersecurity Executive Director, Product Security, Reinsurance Group of America (RGA)
 Registration Level:
- Conference Pass
10:15 am - 10:50 amAs cybersecurity continues to evolve, so does the need for professionals who can seamlessly connect security initiatives with business objectives. Enter the Business Information Security Officer (BISO)—a critical yet often misunderstood role.
In this engaging panel discussion, regional BISOs share insights into their responsibilities, challenges, and the strategic impact they have within their organizations. Whether you’re a technical professional looking to advance your career or an executive seeking to understand the business side of cybersecurity, this session helps demystify the BISO role and its importance in today’s security landscape.
Attendees will gain:
- A clear understanding of what a BISO does and how they differ from CISOs and other security leaders
- Insights into how technical professionals can develop the business acumen necessary to transition into leadership roles
- Practical strategies for bridging the gap between security and business priorities
Join us to explore the intersection of business and security and how mastering both can accelerate your career.
10:15 amChoose Your Own Disaster: Inside General Mills' Multi-Disciplinary Threat Simulations Sr. Director, Cybersecurity, General MillsRegistration Level:
- Conference Pass
10:15 am - 10:50 amWhat happens when a serious threat unfolds and every decision changes what comes next? In this interactive workshop, participants step inside General Mills’ multi-disciplinary threat simulations and explore how security, technology, business, and operational teams respond to complex, high-impact scenarios.
Through a choose-your-own-disaster format, the session examines the tradeoffs, dependencies, and consequences that emerge when teams must act with incomplete information and competing priorities. Attendees will gain practical insight into designing realistic simulations, strengthening cross-functional decision-making, clarifying accountability, and turning exercise outcomes into meaningful improvements in organizational readiness and resilience.
10:15 amAI Is Breaking Data Security… and Fixing It: The New Reality of AI-Driven Risk and How to Stay Ahead Director, Pre-Sales Engineering, Concentric AIRegistration Level:
- Open Sessions
10:15 am - 10:50 amAI is rapidly becoming one of the biggest drivers of productivity and innovation in the enterprise—and one of the fastest-growing sources of data security risk. As copilots, assistants, and public AI tools become integrated into daily work, sensitive data is flowing into systems that most security teams can’t fully see, understand, or control.
The problem is that traditional data security controls were never built for this. In fact, many organizations were already struggling to operationalize data security before AI accelerated the challenge. The good news? AI isn’t just creating the problem—it’s also enabling a smarter, more effective way to solve it.
In this session, attendees will learn:
- Why AI has become one of the fastest-growing and least visible sources of enterprise risk
- How GenAI is creating new exposure points for sensitive data
- Why legacy data security tools have failed to keep up—and why AI is making those gaps harder to ignore
- How context-aware, AI-driven data security can deliver more accurate visibility, stronger controls, and real-time enforcement
- What organizations can do to enable AI innovation without expanding their risk surface
Attendees will leave with a clearer understanding of how AI is reshaping data security—and how they can use that same technology to gain control, minimize exposure, and support safer AI adoption across the business.
10:50 amNetworking BreakRegistration Level:- Open Sessions
10:50 am - 11:10 amLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
11:00 amAdvisory Council Roundtable Discussion (VIP / Invite Only)Registration Level:- VIP / Exclusive
11:00 am - 11:45 amSessions details to come.
Moderated discussion for SecureWorld Advisory Council members. By invite only.
11:10 amThe Open Road to Cyber ResilienceHow Winnebago Industries Turns Security Awareness into a Shared ResponsibilityInformation Security Analyst, Winnebago IndustriesSr. Security Engineer, Winnebago IndustriesVP of Information Security, Winnebago IndustriesRegistration Level:- Conference Pass
11:10 am - 11:45 amIn an era where “black box” security departments are becoming a liability, Winnebago is flipping the script by turning cybersecurity into a high-visibility, collaborative experience. This session takes you behind the scenes of its signature Annual Cyber Resiliency Strategy Event—a high-energy, hands-on day where the barriers between internal teams and external vendor partners vanish.
Discover how they transform a standard training room into a live “security expo,” with interactive stations that demystify the complex tech stacks keeping the company secure. The Winnebago team will break down how this event serves as the cornerstone of their year-round Transparency Strategy. From podcasts and videos to monthly newsletters, learn the specific tactics they use to keep leadership informed, engaged, and invested in the “good” being done by the security team.
11:10 amResilience by Design: Architecting Agentic Systems to Fail Safely, Not Catastrophically Field CISO | Executive in Residence, ZenityRegistration Level:
- Open Sessions
11:10 am - 11:45 amAgentic AI doesn’t fail like traditional software. It reasons past faults, improvises around bad inputs, and keeps acting, which means a single hallucinated data point can cascade through a multi-agent workflow before anyone notices. Most organizations are racing to deploy autonomous agents without architecting for the moment those agents are wrong. This session makes the case that fail-safe design is not a constraint on agentic AI adoption, it’s the precondition for scaling it responsibly.
Drawing on three decades building enterprise security programs and his framework for sustained cyber resilience, Gary Hayslip will lay out a practical architecture for containing agentic AI failure: bounded authority and least-privilege for autonomous actors, circuit breakers at points of irreversible consequence, observable reasoning for post-incident accountability, and designed degradation paths when agents hit ambiguity. Attendees will leave with a concrete framework for evaluating whether their own agentic deployments are built to fail safely and the board-ready language to make the case for the investment before the first incident forces the conversation.
11:10 am[Panel] Navigating the Evolving Digital Battlefield Director, Americas Sales Engineering, Kiteworks
 Registration Level:
- Open Sessions
11:10 am - 11:45 amAs organizational footprints expand across cloud, SaaS, OT/IoT, and dispersed workforces, defenders face a more complex and interconnected digital battlefield. This panel brings together experts to explore how today’s threat actors combine automation, social engineering, identity breaches, and software supply-chain attacks into highly coordinated assaults.
Panelists will examine the expanding importance of identity in the modern SOC, the emergence of AI-driven threats such as automated reconnaissance and deepfake-assisted breaches, and how fourth-party dependencies are changing risk visibility. The discussion also connects these trends to organizational resilience—showing how teams can improve detection, response, and business continuity across an evolving attack surface. This comprehensive session provides practical insights for any security leader seeking clarity amid converging threats.
11:45 amNetworking BreakRegistration Level:- Open Sessions
11:45 am - 12:00 pmLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
12:00 pm[Lunch Keynote] You Be the CISO: A Live AI Breach Exercise Registration Level:
- Conference Pass
12:00 pm - 12:45 pmA customer support rep pastes a batch of unredacted tickets into a free AI chatbot to save twenty minutes on a slow afternoon. Three weeks later, it’s a full-blown incident. This session puts the room in the driver’s seat of exactly that moment. Attendees vote live from their phones at each turning point, from the first technical call on containing the exposure through the investigation, the disclosure decision, and what changes afterward, watching in real time how the room’s instincts split and where they align.
Rather than a lecture on AI risk, this is a hands-on decision exercise that reveals how different roles—technical, investigative, and leadership—each face a different high-stakes call as an incident unfolds, and how those calls compound. Attendees leave with a sharper instinct for how AI-related incidents actually move through an organization, and where the highest-leverage decisions sit at every level, not just the top.
12:45 pmNetworking BreakRegistration Level:- Open Sessions
12:45 pm - 1:15 pmLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
1:15 pmOperation Technology Security: Getting OT Buy-in by Delivering Security Capabilities Director of Cybersecurity, CHS Inc.Registration Level:
- Conference Pass
1:15 pm - 1:50 pmSecuring operational technology (OT) environments is critical to ensuring the safe, reliable, and continued operation of an organization’s most important assets. However, successful OT security requires more than deploying tools or enforcing policies—it depends on building trust, aligning with operational priorities, and delivering capabilities that help OT teams operate more safely and securely. This session explores practical ways to gain OT buy-in by positioning security as an enabler of operational resilience rather than a barrier to productivity.
1:15 pmIdentity Security Beyond MFA: Continuous Verification and Risk-Based ControlsRegistration Level:- Conference Pass
1:15 pm - 1:50 pmSession details to come.
1:15 pm[Panel] The Double-Edged Sword of AI in Cyber Defense Regional Field CTO, Americas, DigiCert
 Panel DiscussionRegistration Level:
- Open Sessions
1:15 pm - 1:50 pmAI is revolutionizing cybersecurity at all levels, speeding up detection and enabling automated attacks on an unprecedented scale. This session examines AI’s dual role as both a powerful defensive tool and a new threat vector for attackers. Panelists will discuss how AI copilots enhance analyst workflows, triage, and anomaly detection, while also addressing emerging risks such as LLM data leakage, prompt injection, model poisoning, and hallucinations within high-trust SOC processes.
The discussion will cover AI governance and assurance frameworks, evolving regulatory expectations, and the impact of synthetic content—including deepfakes, audio spoofing, and hyper-personalized phishing—on social engineering defenses. Attendees will leave with a solid understanding of AI’s potential, the safety measures needed for responsible deployment, and practical steps for preparing teams and pipelines for an AI-driven threat environment.
1:50 pmNetworking BreakRegistration Level:- Open Sessions
1:50 pm - 2:10 pmLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
2:10 pmCybersecurity without the Fortune 500 Budget10 Essential Practices Every Small and Mid-Sized Business Must Master CISO, Data Recognition
 CISO, Land O'Lakes
 Registration Level:
- Conference Pass
2:10 pm - 2:45 pmCybercriminals don’t care how large your business is—they care whether you’re easy to compromise.
This practical session focuses on the 10 cybersecurity practices that provide the greatest reduction in risk for small and mid-sized businesses. Attendees will learn how to defend against ransomware, business email compromise, credential theft, insider threats, and data loss without enterprise-sized budgets or teams.
Leave with a practical roadmap you can begin implementing immediately to strengthen your organization’s cyber resilience. Participants will learn:
- Where SMBs are actually getting attacked today
- Which security investments provide the biggest return
- Techniques for building a cyber program on a limited budget & resources
- How to prepare for the day something goes wrong
- How to build resilience instead of simply buying more technology
2:10 pmQuantum Readiness: Preparing Your Organization for a Post-Quantum FutureRegistration Level:- Conference Pass
2:10 pm - 2:45 pmSession details to come.
2:10 pm[Panel] The Human Layer: Insider Risk, Behavioral Analytics, and the AI Threat MultiplierRegistration Level:- Open Sessions
2:10 pm - 2:45 pmPeople have always been the most targeted layer in any organization’s security posture—but AI is rewriting the rules of engagement. Sophisticated phishing campaigns now arrive personalized at scale, deepfake audio and video are eroding the credibility of internal communications, and MFA fatigue attacks are turning security controls against the users they were designed to protect. The threat surface hasn’t changed, but the speed, precision, and plausibility of attacks targeting it have.
At the same time, defenders are gaining new tools. Behavioral analytics and UEBA platforms are surfacing anomalies that static rules would miss, and AI-assisted policy frameworks are helping organizations govern workforce behavior—including how employees interact with AI tools themselves—without sacrificing productivity. This panel brings together practitioners navigating insider risk, identity-based threats, and the governance questions that arise when the line between human error and AI-augmented deception becomes increasingly hard to draw.
2:45 pmNetworking Break & Cyber ConnectFinal Entries for Dash for Prizes and PassportRegistration Level:- Open Sessions
2:45 pm - 3:00 pmLocation / Room: Networking HallThis is your final chance to visit the Networking Hall and get scanned by our participating partners for our Dash for Prizes. You can also turn in your Passport cards at the Registration Desk before we announce our winner!
3:00 pm[Closing Keynote] Ask Us Anything! A Live Conversation with Security LeadersCISO, CengageDirector, Cybersecurity, Anderson CorporationCISO, Metropolitan Airports CommissionRegistration Level:- Open Sessions
3:00 pm - 3:45 pmLocation / Room: Keynote TheaterIn an industry defined by constant change, some challenges have proven remarkably persistent. New technologies emerge, threat actors adapt, and the latest “revolution” captures headlines—but many of the core issues security leaders face today are the same ones they’ve been navigating for years.
This interactive closing keynote brings together a panel of experienced security leaders for a candid, audience-driven conversation about what hasn’t changed in cybersecurity. From managing risk and influencing the business to building trust, leading teams, and responding to inevitable incidents, the discussion will focus on the enduring lessons that remain relevant—regardless of the tools, platforms, or trends of the moment.
Attendees are encouraged to shape the conversation by asking live questions, sharing reflections, and sharing real-world scenarios. Whether the topic is AI, cloud, ransomware, or the next unknown disruption, this session offers perspective grounded in experience—and a reminder that while technology evolves, the fundamentals of security leadership remain surprisingly constant.
Join us for an honest conversation, shared learning, and a thoughtful end to the day before we continue the discussion at happy hour.
3:45 pmDash for PrizesRegistration Level:- Open Sessions
3:45 pm - 4:15 pmLocation / Room: Networking HallParticipating sponsors will announce their Dash for Prizes winners directly following the closing keynote in the Keynote Theater. Must be present to win.
4:30 pmAnnual End of Year CheerRegistration Level:4:30 pm - 7:00 pmLocation / Room: Mall of America — Studio on 4Join your peers at the Mall of America – Studio on 4 (just down from the SecureWorld conference location at the JW Marriott Minneapolis Mall of America) for the fourth year of the annual tradition, bringing the Twin Cities’ Information Security community together to kick off the holiday season with a social! This is a time to celebrate the power of connection, to reflect on major events of the year, and to contemplate our future together in cybersecurity.
Your hosts this year represent the local Minnesota chapters of ISSA, WiCyS, InfraGard, and MCPA, along with sponsorship from the area’s premier technology and consulting firms. We are also pleased to announce that SecureWorld is partnering with ISSA, WiCyS, InfraGard, and MCPA to deliver this great event at the end of the SecureWorld conference.
Please register separately here for the 4th Annual End of Year Cheer. You are encouraged to attend SecureWorld Twin Cities (register here for the conference) and stay for the holiday party event.
If you are attending both events, you must register for both.

 1PasswordBooth: 440
1Password is a privacy-focused password manager that keeps you safe online. 1Password is the world’s most-loved password manager. By combining industry-leading security and award-winning design, the company provides private, secure, and user-friendly password management to businesses and consumers globally. More than 80,000 business customers, including IBM, Slack, PagerDuty, and GitLab, trust 1Password as their enterprise password manager.
 CriblBooth: 210
Cribl makes open observability a reality for today’s tech professionals. The Cribl product suite defies data gravity with radical levels of choice and control. Wherever the data comes from, wherever it needs to go, Cribl delivers the freedom and flexibility to make choices, not compromises. It’s enterprise software that doesn’t suck, enables techprofessionals to do what they need to do, and gives them the ability to say “Yes.” With Cribl, companies have the power to control their data, get more out of existing investments, and shape the observability future.
Founded in 2018, Cribl is a remote-first company with an office in San Francisco, CA. For more information, visit www.cribl.io or our LinkedIn, Twitter, or Slack community.
 DigiCert, Inc.Booth: 330
As the leading provider of digital trust, DigiCert solutions help you engage online with confidence, knowing your data and connections are secure. From enterprise solutions to software security, identity management to IoT, and DNS to quantum cryptography, DigiCert is trusted around the globe by individuals, businesses, governments, and 90% of Fortune 500 companies.
 DTEXBooth: 100
DTEX is the leader in risk-adaptive security, unifying human, data, and AI risk through a behavioral intelligence platform built for enterprise scale to detect threats early and prevent breaches.
 InfraGard Minnesota Members AllianceBooth: TBD
 ISC2 Twin Cities ChapterBooth: TBD
Our mission is to create a safe environment where information security practitioners can openly share expertise and ideas, providing practical, relevant, useful and timely information that, when applied, will develop and promote the ISC2 CISSP CBK®. help support the Information Security and Cyber Security Communities of the Upper Midwest.
The objectives of this chapter are to:
• Educate: Provide low cost (or no-cost), high impact educational opportunities for both new and seasoned information security practitioners.
• Network: Create an environment that encourages relationship building and professional growth via networking and creating Mentorship opportunities
• Transform: Provide a forum for the free exchange of bold, innovative, transformative ideas to advance the perception and effectiveness of information security. ISSA Minnesota ChapterBooth: TBD
The Minnesota Chapter of ISSA (MN ISSA) serves the Minneapolis / St. Paul twin cities area, greater Minnesota and western Wisconsin. Our membership, over 170 strong and growing, is drawn from the multitude of large corporations, small businesses, government entities and educational institutions in the area. They span all levels of career growth, from students and entry-level to senior management, and cover all industries – finance, medical, government, education, retail, technology, services, and more. This depth of experience and breadth of knowledge provides a dynamic networking environment and a cadre of great individuals to draw from for education, guidance and thought leadership.
 KiteworksBooth: 430
Kiteworks’ mission is to empower organizations to effectively manage risk in every send, share, receive, and save of sensitive content. To this end, we created a platform that delivers content governance, compliance, and protection to customers. The platform unifies, tracks, controls and secures sensitive content moving within, into, and out of their organization, significantly improving risk management and ensuring regulatory compliance on all sensitive content communications.
 MCPA Minnesota ChapterBooth: TBD
The Military Cyber Professionals Association (MCPA) Minnesota Chapter’s mission is to promote regional STEM education as an extension of MCPA national, and to provide a Midwest venue for MCPA members to meet, network, and advance the initiatives of the organization. We are headquartered in Minneapolis, Minnesota. The Chapter President is Lieutenant Colonel Peter Kapelanski. Please find more details on the MCPA member-only intranet.
 NinjaOne LLCBooth: 420
NinjaOne is a Leader in the Gartner Magic Quadrant for Endpoint Management tools, a Leader in two IDC MarketScape reports, and a Champion in the Canalys RMM and PSA Leadership Matrix. NinjaOne is #1 in 14 categories in the G2 Winter Report, including autonomous endpoint management, patch management, RMM, and Online Backup.
 RubrikBooth: 300
Rubrik, the Zero Trust Data Security Company, delivers data security and operational resilience for enterprises. Rubrik’s big idea is to provide data security and data protection on a single platform, including Zero Trust Data Protection, ransomware investigation, incident containment, sensitive data discovery and orchestrated application recovery. This means data is ready at all times so you can recover the data you need and avoid paying a ransom. Because when you secure your data, you secure your applications, and you secure your business.
 Sanity SolutionsBooth: 110
Headquartered in Denver, CO since 2004, Sanity Solutions specializes in comprehensive solutions and services for your IT and data management needs. More than a value-added reseller (VAR), we take a personalized approach by identifying your unique business needs and creating strategic goals and technical solutions to maximize your investments and results.
 ThreatLockerBooth: 410
ThreatLocker® is a global cybersecurity leader, providing enterprise-level cybersecurity tools to improve the security of servers and endpoints. ThreatLocker’s combined Application Whitelisting, Ringfencing™, Storage Control, and Privileged Access Management solutions are leading the cybersecurity market towards a more secure approach of blocking unknown application vulnerabilities. To learn more about ThreatLocker visit: www.threatlocker.com
 WiCyS Minnesota AffiliateBooth: TBD
WiCyS offers mentoring, learning, networking and career development to women at all stages of their cybersecurity careers. Whether you are a student just considering a career in cybersecurity, or an experienced leader in the cybersecurity workforce, WiCyS provides tangible benefits and a supportive community.
The Women in Cybersecurity Minnesota (WiCyS MN) is a regional affiliate that covers these geographic areas: Minnesota with outreach into Wisconsin, Iowa, North and South Dakota. As a WiCyS Affiliate, we will undertake activities to promote recruitment, retention, and advancement of women in cybersecurity.
 ZenityBooth: 320
Zenity.io, a cybersecurity company founded in 2021 and based in Tel Aviv, Israel, specializes in securing and governing enterprise AI agents and low-code/no-code development. It provides a security governance platform that scans environments to identify AI applications, bots, and copilots, assessing risks like data access and security misconfigurations. The platform offers real-time monitoring, automated compliance, and shadow IT management. Zenity has raised significant funding, including a $38 million Series B round led by Third Point Ventures and DTCP, and an investment from Microsoft’s Venture Fund, M12.
- Ahanu BoyleCyber Risk Analyst, Cyber Risk Opportunities LLC
Ahanu is a cyber risk analyst with Cyber Risk Opportunities who brings years of hands-on information security experience to the enterprise AI challenge. They lead cyber risk management initiatives for organizations of all sizes, translating complex security concepts into actionable strategies that business leaders can implement.
Since the emergence of generative AI, Ahanu has been at the forefront of enterprise AI security helping organizations safely integrate LLMs into their operations without sacrificing productivity or innovation. Their specialty lies in building secure AI workflows that actually work in practice, bridging the gap between cutting-edge technology and real-world business needs.
Ahanu’s approach centers on a core belief: effective security enables innovation rather than blocking it.
- Tom PohlMember, InfraGard Iowa Members Alliance
- Cameron H. MalinCyber Behavioral Profiler, FBI (Ret.) and Modus Cyberandi
Cameron Malin, JD, CISSP, is the founder of Modus Cyberandi, a bespoke Cyber Behavioral Profiling consultancy specializing in the assessment of cyber threat actor decision making, adversary tradecraft, cyber deception, and cognitive vulnerabilities. As a retired Behavioral Profiler with the Federal Bureau of Investigation (FBI), he has more than 22 years of experience investigating, analyzing, and profiling cyber adversaries across the spectrum of criminal to national security attacks.
During his tenure in the FBI, he was the founder of both the FBI Behavioral Analysis Unit's (BAU) Cyber Behavioral Analysis Center (CBAC), the FBI BAU's methodology and application of science-based behavioral profiling and assessment to national security and criminal cyber offenders—and the BAU’s Deception and Influence Group (DIG), a uniquely trained and experienced cadre of Behavioral Profilers specialized in analyses and countermeasures to adversary cyber deception campaigns and influence operations.
He is a co-author of the authoritative cyber deception book, "Deception in the Digital Age: Exploiting and Defending Human Targets Through Computer-Mediated Communications" (published by Academic Press, an imprint of Elsevier, Inc.), and co-author of the Malware Forensics book series: "Malware Forensics: Investigating and Analyzing Malicious Code," "Malware Forensics Field Guide for Windows Systems," and "Malware
Forensics Field Guide for Linux Systems" (all published by Syngress, an imprint of Elsevier, Inc.). - Chad WalkerExecutive Director, Product Security, Reinsurance Group of America (RGA)
Chad is Executive Director of Product Security at Reinsurance Group of America (RGA). Prior to his current role, he was a BISO and a leader of BISOs for multiple Fortune 100 companies. He has seen firsthand how BISO programs can succeed or fail in their mission of improving cybersecurity programs and driving adoption of secure delivery patterns across the enterprise.
- Matt CelichowskiBISO, Sr. Director of Information Security, W.W. Grainger, Inc.
- Billie ChockSr. Director, Cybersecurity, General Mills
Billie Chock is Senior Director of Cyber Security at General Mills, where she leads enterprise cybersecurity strategy, governance, risk, and defense initiatives. A United States Marine Corps (USMC) veteran, Billie brings broad technology leadership experience, including serving as a business segment CIO, before moving into cybersecurity. That cross-functional background informs her practical approach to connecting security, technology, business, and operational perspectives. In this workshop, Billie shares lessons from General Mills’ multi-disciplinary resilience-building simulations, showing how organizations can prepare for complex, high-impact threats and translate realistic scenarios into stronger readiness, clearer accountability, and more confident response and enduring organizational confidence.
- Jim RobertsonDirector, Pre-Sales Engineering, Concentric AI
Jim has 10+ years in the data security space and has been an Sales Engineer at Varonis, StealthBits (Netwrix), Splunk, IBM, and Bionic AI. Before that, he served in network and systems engineering roles at MSPs in the upper Midwest. His broad experience in deploying and securing systems and data has translated into thought leadership about the practical challenges in the data security posture management space.
- Patricia CammerrerInformation Security Analyst, Winnebago Industries
Patricia Cammerrer is an Information Security Analyst at Winnebago with more than 20 years of technology experience and five years focused on cybersecurity. As a member of the Security Operations Center (SOC) team, she investigates security incidents, supports threat detection and response efforts, and helps strengthen the organization's security posture. Patricia is passionate about cybersecurity awareness and plays an active role in Winnebago's annual Cybersecurity Awareness Month (CSAM) events, creating engaging educational experiences that promote a culture of security.
- Alex GregorSr. Security Engineer, Winnebago Industries
Alex Gregor is a Senior Security Engineer with expertise in designing, implementing, and managing enterprise security solutions that reduce risk and strengthen organizational resilience. Experienced in security architecture, vulnerability management, compliance, and security operations, with a strong focus on aligning cybersecurity initiatives to business objectives. Trusted partner to IT and business stakeholders, driving security best practices, risk mitigation, and continuous improvement across complex environments.
- Kristi YauchVP of Information Security, Winnebago Industries
Kristi Yauch is Vice President of Information Security at Winnebago Industries, where she leads enterprise cybersecurity, cyber resilience, risk management, and security awareness initiatives. With over two decades of experience in IT and cybersecurity leadership, she has a proven track record of building high-performing security programs that protect organizations while enabling innovation and growth.
A strong advocate for making cybersecurity accessible and relevant to all employees, Kristi is passionate about fostering a resilient security culture through education, transparency, and collaboration. Her experience spans security operations, incident response, governance, compliance, disaster recovery, and security architecture. She frequently works with executives, business leaders, and technology teams to integrate cybersecurity into everyday business decisions and operations.
- Gary R. HayslipField CISO | Executive in Residence, Zenity
Gary Hayslip is an experienced global security executive with a proven track record of delivering innovative security programs that protect billion-dollar enterprises at every touchpoint. He is intensely focused on driving continuous improvement to maximize the efficiency of security programs while minimizing costs. As an insightful thought leader, he possesses strong business acumen and a commitment to organizational mission, values, and goals. He has demonstrated the ability to collaborate with all levels of an organization to champion new ideas, gain buy-in and build consensus. Hayslip brings extensive experience in information technology, cybersecurity operations, security architecture & strategy, physical security, and risk management to his role as the Field CISO | CISO in Residence for Zenity.io. His previous executive positions include multiple roles as Chief Information Security Officer, Chief Information Officer, Field CISO, and Operating Partner for the U.S. Navy (Active Duty), the U.S. Navy (Federal Government employee), the City of San Diego, California, Webroot Software, SoftBank Investments (Vision Fund & Vision Fund II), and Halcyon Security.
Hayslip is a proven cybersecurity expert who has earned a reputation as a highly effective communicator, author, and keynote speaker. He co-authored the “CISO Desk Reference Guide: A Practical Guide for CISOs – Volumes 1 & 2,” “The Executive Primer: An Executive’s Guide to Security Programs,” “Developing Your Cybersecurity Career Path,” and the “The Essential Guide to Cybersecurity for SMBs.” He recently coauthored and published “Mastering Third Party Risk,” a guide aimed specifically for security practitioners to help them manage the risk exposure to organizations from vendors and supply chains. These books are among the top resources for helping CISOs improve their leadership and business skills. Hayslip currently serves as an independent director on several boards and advises security and technology firms. He is an active member of the cybersecurity community and belongs to professional organizations such as ISC2, NACD, ISACA, and Infragard. Hayslip holds several professional certifications, including CISSP, CISA, and CRISC, and has earned a BS in Information Systems Management from the University of Maryland and an MBA from San Diego State University.
- Cátia PereiraDirector, Americas Sales Engineering, Kiteworks
Catia Pereira leads the Americas Sales Engineering team at Kiteworks, a cybersecurity platform purpose-built to give organizations granular control over how sensitive data is shared, accessed, and governed - enforcing policy-driven data exchange across every communication channel through a unified policy engine. With growing regulatory complexity and the rapid adoption of AI, Kiteworks helps organizations ensure that private data remains protected, compliant, and auditable whether it's being exchanged between people, systems, or AI workflows. Catia partners with organizations of all sizes, from emerging growth companies to large enterprises, helping them reduce private data risk and navigate the intersection of secure data exchange, compliance, and AI governance.
Before joining Kiteworks, Catia worked in Fintech, at a leading financial data and analytics platform, helping financial institutions analyze large volumes of highly sensitive market data and proprietary research. Recognizing that most organizations lacked a unified, enterprise-wide solution to govern private data communications end-to-end sparked her transition into the broader security space - and ultimately to Kiteworks.
- Jayson NelsonCISO, MCG Energy Solutions, LLC
- Jonathan MayCISO, Mortenson
Jonathan May is a strategic information security leader focused on building and advancing security programs that move beyond simply defending the business to enabling it to navigate uncertainty, embrace innovation, and move faster with confidence. As the leader of Information Security at Mortenson, he leads the strategy and execution of cybersecurity initiatives, translating complex cybers risks into tactical, business-focused strategies that enable growth, strengthen capability, and drive informed decision-making. Jonathan believes effective security is not simply about reducing risk—it’s about preparing organizations to be more resilient, more adaptable, and better positioned to move confidently and securely into the future.
- Aaron De BoerDirector of Cybersecurity, CHS Inc.
Aaron is the Director of Cyber Security for CHS Inc., where he leads the security engineering and security operations teams that work to secure the enterprise. Aaron has more than two decades of experience in technology, security engineering, and leadership roles in insurance, manufacturing, agriculture, and energy.
- Tim McAllisterRegional Field CTO, Americas, DigiCert
Tim McAllister is Regional Field CTO Americas in DigiCert's Office of the CTO. With more than 20 years of senior leadership experience, he works with enterprises and original equipment manufacturers to turn digital trust requirements into deployable architectures and operating models. His areas of focus include PKI and certificate lifecycle management, AI trust and machine identity, device and software trust, post-quantum cryptography, and security for connected and critical systems. Tim is also an active industry and standards strategist, with experience spanning healthcare, industrial and energy environments, electric vehicle infrastructure, and other high-assurance use cases.
- Aimee MartinCISO, Data Recognition
- Tony TaylorCISO, Land O'Lakes
Tony Taylor is Chief Information Security Officer at Land O'Lakes, Inc., where he leads the enterprise cybersecurity program responsible for safeguarding the company’s global digital ecosystem, including the technologies that support modern agriculture, food production, and supply chain operations.
Tony brings more than 30 years of leadership experience spanning enterprise infrastructure, cybersecurity strategy, and risk management. Over the course of his career, he has led technology and security organizations across several highly regulated and operationally complex industries, including insurance, energy, manufacturing, agriculture, and consumer goods. His leadership focuses on building resilient cybersecurity programs that align with business strategy while protecting organizations operating within critical infrastructure sectors.
In addition to his corporate leadership role, Tony is deeply engaged in the broader technology leadership community. He serves as Chapter Chair for InspireCIO and is a Governing Body member of Evanta, where he collaborates with fellow CIOs and CISOs to advance leadership practices and cybersecurity strategy.
Tony is a frequent speaker at industry and executive forums, sharing insights on cybersecurity governance, emerging threats, enterprise resilience, and the evolving role of the CISO in protecting organizations in an increasingly interconnected world.
- Tina MeekerDeputy CISO, Old Republic
- Mea CliftCISO, Cengage
Mea Clift is the Chief Information Security Officer (CISO) at Cengage, a seasoned cybersecurity executive known for aligning security strategy with enterprise risk and resilience. With decades of experience, she specializes in governance, risk, and compliance (GRC), helping organizations navigate complex threats and translate technical risk into clear business value.
One of the top 25 Cybersecurity Women of the World for 2026, and a 2025 honoree of the Women in IT Security awards, Mea is widely recognized for her leadership, mentorship, and advocacy for inclusion in cybersecurity. Mea is also the creator of the GRC Intensive Program, a 14 week hands-on educational program to teach the "how" of GRC to cybersecurity practitioners.
Outside of her professional work, she is a passionate quilt historian and educator, and lives in St. Paul, Minnesota, with her greyhounds, combining her love of textiles with a deep commitment to community and creativity.
- Frank RossDirector, Cybersecurity, Anderson Corporation
Frank Ross is Director of Cybersecurity at Andersen Corporation, with previous experience leading Enterprise Information Security and Enterprise Architecture. He specializes in business enablement, data protection, and defensible architecture while empowering teams to deliver secure and effective technology solutions. Frank brings a strong focus on aligning security strategy with organizational goals and operational excellence.
- Aaron Verdell CallCISO, Metropolitan Airports Commission
- Emily KedingSr. Director, IT Infrastructure & Cybersecurity, Restaurant Technologies
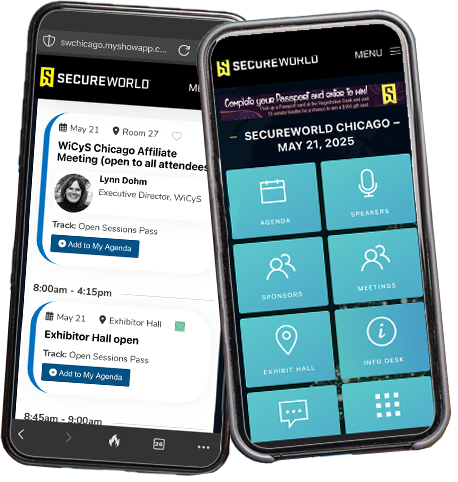
Easily navigate your conference experience and make the most of your day with a dedicated conference app!
- Streamline event check-in
- Discover relevant topics and speakers
- Find your way with interactive venue maps
- Connect with fellow attendees
- View speaker presentation slides (post-event)
- Download a Certificate of Attendance
Propel your cyber career at SecureWorld! Grow your skills and connect with local security peers.
