SecureWorld conferences blend world-class keynotes, breakout sessions, small group discussions, and opportunities to earn CPE credits.
-
 Cybersecurity Director, GFT
 EVP, CISO, Equifax
 CISO / CIO, Esquire Deposition Solutions, LLC
-
 Global Director, Governance, Risk & Compliance, Genuine Parts Company
-
 State CISO, State of Georgia
 Open Sessions
 Conference Pass
 SecureWorld Plus
 VIP / Exclusive
- Wednesday, September 23, 20269:00 am[PLUS Course] Securing & Enabling AI: Transform Chaos into Competitive Advantage
 Registration Level:
- SecureWorld Plus
9:00 am - 3:00 pmLocation / Room: Concourse NorthYour CEO just asked about AI security. Do you have a clear answer?While you’re counting vulnerabilities, your competitors are deploying AI at scale.While security teams are still cataloging vulnerabilities, business units are deploying AI at scale. Marketing is using generative AI for campaigns. Sales is rolling out AI SDRs. Customer service is automating with chatbots.Every Monday, another department launches an AI tool. Marketing uses ChatGPT for campaigns. Sales deploys AI Sales Development Reps. Customer service automates with chatbots. And your cybersecurity team? Still writing policies nobody reads.In this interactive workshop, learn you how to secure AI while accelerating innovation—not blocking it. Transform from AI Firefighter to Strategic Business Enabler, with a 90-day roadmap for secure AI deployment in your organization.What You’ll Master-
The AIR-MAP Methodology™ — Your proven 90-day roadmap from AI chaos to governance
-
Executive Translation — Turn technical AI risks into boardroom language
-
NIST AI RMF Implementation — Practical application, not theory
-
The $12M Question — Secure against deepfake fraud and AI-enabled attacks
-
Shadow AI Discovery — Find and govern the AI already in your organization
-
Business-First Security — Protect value, not just systems
Who Should AttendIdeal for:-
CISOs facing board questions about AI
-
Information Security Directors enabling digital transformation
-
IT VPs without dedicated security teams
-
Cybersecurity Consultants serving enterprise clients
-
Risk Managers governing AI initiatives
-
Aspiring decision makers and those reporting to one
Not designed for:-
Developers wanting to code AI models
-
Analysts seeking technical certifications
-
Anyone looking for hands-on hacking labs
What This Workshop Is (and Isn’t)This workshop is NOT about:-
Prompt injection techniques
-
Model architecture security
-
Technical vulnerability scanning
-
Writing 200-page policies
This workshop IS about:-
Speaking profit-and-loss to executives
-
Enabling your AI transformations
-
Building cybersecurity into AI from day one
-
Becoming the trusted AI advisor
What You’ll Leave With1. The Complete AIR-MAP Toolkit-
90-day implementation roadmap
-
Discovery templates and workflows
-
Risk scoring calculators
-
Executive presentation templates
2. Ready-to-Deploy Governance Assets-
AI Acceptable Use Policy (customize in minutes)
-
Vendor assessment questionnaires
-
Incident Response playbooks
3. A 30-Minute Strategy SessionA complimentary private consultation to apply AIR-MAP directly to your organization’s AI strategy and risk posture. - Thursday, September 24, 20267:30 amRegistration openRegistration Level:
- Open Sessions
7:30 am - 4:15 pmLocation / Room: Registration Desk (Ballroom Pre-Function)Come to the Registration desk in the lobby to check-in and get your badge. SecureWorld staff will be available throughout the day if you have any questions.
8:00 amNetworking Hall openRegistration Level:- Open Sessions
8:00 am - 4:45 pmLocation / Room: Networking HallYour opportunity to visit our solution vendor partners, whose sponsorship makes SecureWorld possible, as well as association chapters! Booths have staff ready to answer your questions. Look for participating Dash For Prizes sponsors to be entered to win prizes.
Also, look for “Cyber Connect” discussions on select topics and join the conversation.
8:00 amISSA Atlanta Chapter Meeting [Open to all attendees]The Business of Being Human: The Leadership Edge AI Can Never Replace Chief Development Officer, TekStream; Author, "The Heart of Networking" (Third Edition)Registration Level:
- Open Sessions
8:00 am - 8:45 amLocation / Room: MercerNow that many in our profession are working from home either part-time or full-time, it is more challenging than ever to meet new people and develop meaningful relationships. Whether you are seeking the next step in your career, looking for ways to expand your knowledge and grow in other aspects of cybersecurity, or meeting people in other industry sectors, Ricky’s real-world guidance will be valuable.
8:00 amISC2 Atlanta Chapter Meeting [Open to all attendees]AI Agents Gone Rogue: A Deep Dive into CSA AICMv1.1 President, ISC2 AtlantaRegistration Level:
- Open Sessions
8:00 am - 8:45 amLocation / Room: Concourse NorthSession details to come.
8:00 amAdvisory Council Roundtable Breakfast (VIP / Invite only)The AI Governance Reality Check Registration Level:
- VIP / Exclusive
8:00 am - 8:45 amLocation / Room: Concourse SouthAI has moved faster than most governance programs can keep pace with, and this roundtable brings security leaders together for an honest conversation about what’s actually working to govern it—and where the exposure still lives. Rather than another discussion about policy documents, expect real talk on shadow AI usage, the rise of agentic tools acting with growing autonomy, and the practical challenge of protecting data across different LLMs and the custom AI tools employees are adopting on their own.
8:45 amNetworking BreakRegistration Level:- Open Sessions
8:45 am - 9:00 amLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
9:00 am[Opening Keynote] The AI Train Isn't Stopping—What Cybersecurity Does NextCybersecurity Director, GFTEVP, CISO, EquifaxRegistration Level:- Open Sessions
9:00 am - 9:45 amLocation / Room: Keynote TheaterAI isn’t slowing down. It’s writing code. Agents are showing up in tools your team never approved. Whatever hesitation exists in the boardroom about cost or risk, the train keeps moving—fast, and often in directions nobody sees until they’ve already arrived. The question isn’t whether AI keeps accelerating. It’s what we do while it does.This opening keynote brings security leaders together for a candid, unscripted conversation about the tensions nobody has fully resolved: Can you argue some jobs shouldn’t be replaced by AI and still stay competitive? What guardrails do we actually need when adoption outpaces governance? How do you enable AI agents—web-based, local, or buried in third-party tools—without losing visibility into your own data? No hype, no vendor spin—just an honest look at a moment of real uncertainty, and the kind of peer conversation that sends everyone home with more clarity than they came in with.9:45 amNetworking BreakRegistration Level:- Open Sessions
9:45 am - 10:15 amLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
10:15 amThe Liability You Didn't Sign Up For: Third-Party Risk and Breach Readiness Partner & Chief Cybersecurity Legal Officer (CCLO), Mandelbaum Barrett PCRegistration Level:
- Conference Pass
10:15 am - 10:50 amLocation / Room: Concourse SouthAs organizations increasingly rely on third-party vendors, liability no longer stops at the edge of your network. This session examines the legal and operational realities of distributed digital risk—from vendor contracts and disclosure obligations to indemnification terms and incident transparency requirements. It then turns to breach preparedness itself: what notification deadlines actually demand, why data tracking matters long before an incident occurs, and how the cost and delay of post-breach data mining can quietly derail response timelines. Attendees will leave with a clearer framework for evaluating vendor risk exposure and tightening the gap between breach discovery and legal obligation.
10:15 am[Panel] Cyber Insurance in Today's New World Regional Director, Cyber/Professional Liability - Midsouth Region, USI Insurance
 Southeast Regional Cyber Manager, Bowhead Specialty
 SVP, Global Chief Security Officer, Blue Yonder
 Registration Level:
- Conference Pass
10:15 am - 10:50 amLocation / Room: MercerToday’s challenges are based on modernization, cloud native, adoption of AI, and more. What people often don’t think about is their overall cyber insurance, the benefits, the trade-offs, and how to leverage trends being used to help you in the industry navigate some of these areas. Our session will give you real-world information to think about your cyber insurance, the lens of a CISO and how we think about insurance, and then what are the impacts we are also seeing in the industry.
10:15 amBuilding a Timeless SOC with Cisco & Splunk Sr. Solutions Architect, C1Registration Level:
- Open Sessions
10:15 am - 10:50 amLocation / Room: Concourse NorthIn the ancient world, the strength of a city lay not just in its walls but in the equanimity and readiness of its defenders. Today, the “walls” are fluid, and the defenders are facing a digital siege characterized by “data gravity” and a new workforce of autonomous AI agents.
In this session, we’ll explore how to bridge 10+ years of traditional infrastructure with the future of Agentic AI. We will dive into the Cisco + Splunk synergy, moving beyond simple log ingestion to a unified “Data Fabric” that powers proactive orchestration. Learn how to architect a SOC that remains timeless—balancing the human element of security with autonomous agents that detect, reason, and act at machine speed.
10:50 amNetworking BreakRegistration Level:- Open Sessions
10:50 am - 11:10 amLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
11:10 amThe Cybersecurity (R)Evolution: Secure Programs for Less Money, Less ComplexityGlobal Director, Governance, Risk & Compliance, Genuine Parts CompanyRegistration Level:- Conference Pass
11:10 am - 11:45 amLocation / Room: Concourse SouthWith the continued increase in cyber security incidents, it is apparent that the legacy approach to security is failing. This reality is often met with increasing scrutiny from executive leadership on how much is being spent on security with no apparent Return on Investment. This session will share a thought-provoking method to shift the legacy security paradigm to an evolutionary approach that can lead to an increased security posture for less money and less complexity by focusing on the unique threats and risks to your business.
11:10 amFrom Reactive Management to Autonomous Endpoint Resilience Associate Director of Enterprise Business Support for Americas, ManageEngineRegistration Level:
- Open Sessions
11:10 am - 11:45 amLocation / Room: Concourse NorthEndpoint management is evolving beyond simply detecting problems and responding to them. Explore how AI-powered intelligence, continuous risk prioritization, and automated remediation can help organizations anticipate issues, strengthen resilience, and enable endpoints to recover with greater autonomy. The session will focus on:
- Harness endpoint intelligence to identify patterns, predict potential issues, and drive smarter actions.
- Prioritize the risks that matter most through continuous exposure management and automate remediation at scale.
- Build a more autonomous endpoint environment that can identify disruptions, take corrective action, and restore operations with minimal human effort.
11:10 am[Panel] Navigating the Evolving Digital Battlefield VP of Strategic Accounts, Seceon
 Security Advisory Lead, Splunk, a Cisco Company
 VP, Sales Engineering, P0 Security
 Chief Marketing Officer, Legit Security
 Registration Level:
- Open Sessions
11:10 am - 11:45 amLocation / Room: MercerAs organizational footprints expand across cloud, SaaS, OT/IoT, and dispersed workforces, defenders face a more complex and interconnected digital battlefield. This panel brings together experts to explore how today’s threat actors combine automation, social engineering, identity breaches, and software supply-chain attacks into highly coordinated assaults.
Panelists will examine the expanding importance of identity in the modern SOC, the emergence of AI-driven threats such as automated reconnaissance and deepfake-assisted breaches, and how fourth-party dependencies are changing risk visibility. The discussion also connects these trends to organizational resilience—showing how teams can improve detection, response, and business continuity across an evolving attack surface. This comprehensive session provides practical insights for any security leader seeking clarity amid converging threats.
11:45 amNetworking BreakRegistration Level:- Open Sessions
11:45 am - 12:00 pmLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
12:00 pm[Lunch Keynote] You Be the CISO: A Live AI Breach Exercise Registration Level:
- Open Sessions
12:00 pm - 12:45 pmLocation / Room: Keynote TheaterA customer support rep pastes a batch of unredacted tickets into a free AI chatbot to save twenty minutes on a slow afternoon. Three weeks later, it’s a full-blown incident. This session puts the room in the driver’s seat of exactly that moment. Attendees vote live from their phones at each turning point, from the first technical call on containing the exposure through the investigation, the disclosure decision, and what changes afterward, watching in real time how the room’s instincts split and where they align.
Rather than a lecture on AI risk, this is a hands-on decision exercise that reveals how different roles—technical, investigative, and leadership—each face a different high-stakes call as an incident unfolds, and how those calls compound. Attendees leave with a sharper instinct for how AI-related incidents actually move through an organization, and where the highest-leverage decisions sit at every level, not just the top.
12:00 pmAdvisory Council Roundtable Lunch (VIP / Invite only)Achieving True Resilience in the AI Era Registration Level:
- VIP / Exclusive
12:00 pm - 12:45 pmLocation / Room: Concourse SouthIn the cybersecurity arena, AI technology presents new possibilities for both defenders and attackers. The key to withstanding the next evolution of cyber threats? A resilient identity infrastructure.
Whether your organization uses a specific vendor tool or runs a mix of systems and solutions, identity is your digital foundation of trust. If identity is compromised, your organization’s ability to operate is at risk.
Join this closed-door, invitation-only, peer-to-peer discussion to learn insights and practical strategies for building your identity, cyber, and business resilience. This open forum exchange explores:
- What does it take to plan for true cyber resilience?
- What happens when your identity infrastructure is under attack?
- How do you manage the complexities of a hybrid identity environment?
- How can security, identity, IT, and business leaders work together to ensure resilience across the entire cyber lifecycle?
This session is generously sponsored by:
 12:45 pmNetworking BreakRegistration Level:
- Open Sessions
12:45 pm - 1:15 pmLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
1:15 pmCyversity Atlanta Chapter Meeting: From BISO to the Boardroom: Charting an Executive Pathway to CISOCyversity Atlanta Chapter Meeting (Open to all attendees) BISO, AT&T
 BISO, Boston Consulting Group
 BISO, NCR Voyix
 BISO, Deluxe
 Registration Level:
- Conference Pass
1:15 pm - 1:50 pmLocation / Room: Concourse SouthAs organizations scale their security programs, the Business Information Security Officer (BISO) role has emerged as a critical bridge between business strategy and cybersecurity leadership—and increasingly, a proving ground for the C-suite. This panel of senior security leaders explores how BISOs enable CISOs to scale security across the enterprise, what the role actually looks like day-to-day, the skills and relationships that make a BISO successful, and how the role can serve as a powerful pathway to the CISO seat.
Presented as part of Cyversity Atlanta’s ongoing commitment to building a diverse and inclusive cybersecurity talent pipeline from entry-level to the C- suite, this session offers career-defining insights for cybersecurity professionals. Panelists will share their personal journeys into the BISO seat, the strategic value the role delivers to the business, common misconceptions about the position, and advice for those aiming to follow a similar path into executive security leadership.
Attendees will walk away with:
- A clear understanding of the BISO role and how it differs from—and complements—the CISO function
- Insight into the competencies and experiences that prepare professionals for BISO and eventual CISO roles
- Real talk on navigating career pivots, sponsorship, and visibility in security leadership
- Actionable guidance for building their own pathway to executive cybersecurity roles
1:15 pm[Panel] The Double-Edged Sword of AI in Cyber Defense CEO & Co-Founder, StrongestLayer
 Sales Engineer, Torq
 Director of Cyber Resilience, Field Solution Architects, Everpure
 Registration Level:
- Open Sessions
1:15 pm - 1:50 pmLocation / Room: MercerAI is revolutionizing cybersecurity at all levels, speeding up detection and enabling automated attacks on an unprecedented scale. This session examines AI’s dual role as both a powerful defensive tool and a new threat vector for attackers. Panelists will discuss how AI copilots enhance analyst workflows, triage, and anomaly detection, while also addressing emerging risks such as LLM data leakage, prompt injection, model poisoning, and hallucinations within high-trust SOC processes.
The discussion will cover AI governance and assurance frameworks, evolving regulatory expectations, and the impact of synthetic content—including deepfakes, audio spoofing, and hyper-personalized phishing—on social engineering defenses. Attendees will leave with a solid understanding of AI’s potential, the safety measures needed for responsible deployment, and practical steps for preparing teams and pipelines for an AI-driven threat environment.
1:15 pmIs this Identity Still Human? Identity Activity in Production Environments CEO, ClearVectorRegistration Level:
- Open Sessions
1:15 pm - 1:50 pmLocation / Room: Concourse NorthProduction now runs on identity rather than infrastructure, and 91% of the identities operating in production are non-human. The 2026 ClearVector Identity Intelligence Report puts numbers on that: 80% of non-human activity happens outside business hours, and 3% is destructive, compared with less than 1% for humans. Nearly every security dollar still protects the 9% who are people.
AI widens the gap. Agents now create other agents and issue new identities, and any employee can hand credentials to an LLM that then operates with full access.
John Laliberte, CEO of ClearVector, walks through the report’s findings and the question his customers now ask: is this identity still human, or is an LLM operating behind the account? Attendees will learn how to:
- Quantify non-human and third-party identity risk already in production
- Separate AI-driven activity from the human identity that authenticated
- Set guardrails so agents can only do what you expect
1:50 pmNetworking BreakRegistration Level:- Open Sessions
1:50 pm - 2:10 pmLocation / Room: Networking HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
2:10 pmDisgruntled Employees to Deepfaked Identities: Navigating Insider Response VP, Research Director, Forrester ResearchRegistration Level:
- Conference Pass
2:10 pm - 2:45 pmLocation / Room: Concourse SouthInsider threat presents a unique challenge to organizations, one that requires a different and discrete response across multiple functions. This session will detail the essential elements of insider threat response and help attendees define an escalation path for insider incidents and clarify roles and responsibilities between security, legal, HR, and third parties during an insider incident.
2:10 pmModels Reason, APIs Act: Defending the API Attack Surface in the Agentic Era Security Technology Strategy Director, AkamaiRegistration Level:
- Open Sessions
2:10 pm - 2:45 pmLocation / Room: Concourse NorthAs enterprises connect AI agents to sensitive data, tools, and workflows, familiar API risks begin moving at machine speed. Shadow interfaces multiply, legitimate credentials can produce unintended outcomes, and individually valid requests can add up to dangerous behavior. In this session, you’ll learn how to discover AI- and MCP-related interfaces, identify sensitive data and posture risks, test APIs before production, and detect suspicious runtime behavior. Walk away with a practical view of where API security fits as AI moves from answering questions to taking action.2:10 pm[Panel] The Human Layer: Insider Risk, Behavioral Analytics, and the AI Threat Multiplier Principal Solutions Architect, MGT
 Sr. Solutions Architect, eSentire
 Registration Level:
- Open Sessions
2:10 pm - 2:45 pmLocation / Room: MercerPeople have always been the most targeted layer in any organization’s security posture—but AI is rewriting the rules of engagement. Sophisticated phishing campaigns now arrive personalized at scale, deepfake audio and video are eroding the credibility of internal communications, and MFA fatigue attacks are turning security controls against the users they were designed to protect. The threat surface hasn’t changed, but the speed, precision, and plausibility of attacks targeting it have.
At the same time, defenders are gaining new tools. Behavioral analytics and UEBA platforms are surfacing anomalies that static rules would miss, and AI-assisted policy frameworks are helping organizations govern workforce behavior—including how employees interact with AI tools themselves—without sacrificing productivity. This panel brings together practitioners navigating insider risk, identity-based threats, and the governance questions that arise when the line between human error and AI-augmented deception becomes increasingly hard to draw.
2:45 pmNetworking Break & Cyber ConnectFinal Entries for Dash for Prizes and PassportRegistration Level:- Open Sessions
2:45 pm - 3:00 pmLocation / Room: Networking HallThis is your final chance to visit the Networking Hall and get scanned by our participating partners for our Dash for Prizes. You can also turn in your Passport cards at the Registration Desk before we announce our winner!
3:00 pm[Closing Keynote] Why Incident Response Begins with Relationships, Not RunbooksState CISO, State of GeorgiaRegistration Level:- Open Sessions
3:00 pm - 3:45 pmLocation / Room: Keynote TheaterModern cyber incidents move faster than traditional response models can often support. With adversaries capable of moving from initial access to lateral movement in seconds, organizations can no longer rely on incident response processes assembled after confirmation.
This talk argues that effective incident response begins before the alert fires—in the relationships among security, IT, identity, cloud, legal, communications, vendors, business owners, and executive leadership. Runbooks matter, but relationships determine whether an organization can make decisions, authorize containment, communicate clearly, and protect critical services under pressure.
The session introduces Continuous Incident Response, decision latency, and mean time to decide as practical concepts for evaluating cyber resilience. Attendees will learn why tabletop exercises should test decision velocity, why pre-authorized response actions matter, and why speed is ultimately a governance outcome, not just a technical capability.
3:45 pmHappy Hour & Dash for PrizesSponsored by Concentric AIRegistration Level:- Open Sessions
3:45 pm - 4:45 pmLocation / Room: Ballroom Pre-FunctionJoin your peers for conversation and complimentary beverages. This is a great opportunity to network with other security professionals from the area and discuss the hot topics from the day.
Participating sponsors will announce their Dash for Prizes winners. Must be present to win.
Generously sponsored by:

 1PasswordBooth: TBD
1Password is a privacy-focused password manager that keeps you safe online. 1Password is the world’s most-loved password manager. By combining industry-leading security and award-winning design, the company provides private, secure, and user-friendly password management to businesses and consumers globally. More than 80,000 business customers, including IBM, Slack, PagerDuty, and GitLab, trust 1Password as their enterprise password manager.
 Akamai TechnologiesBooth: 130
Akamai powers and protects life online. Leading companies choose Akamai to build, deliver, and secure digital experiences. With the most distributed compute platform—cloud to edge—customers can build modern apps while keeping experiences closer to users and threats farther away. Learn about Akamai’s security, compute, and delivery solutions at akamai.com.
 AppOmniBooth: 400
AppOmni SaaS security helps security and IT teams protect and monitor their entire SaaS environment, from each vendor to every end-user.
 Arctic Wolf NetworksBooth: 140
Arctic Wolf Networks provides SOC-as-a-service that is redefining the economics of security. The AWN CyberSOC™ service is anchored by Concierge Security™ teams and includes 24×7 monitoring, custom alerting, and incident investigation and response. There is no hardware or software to purchase, and the end-to-end service includes a proprietary cloud-based SIEM, threat intelligence subscriptions and all the expertise and tools required. For more information about Arctic Wolf, visit https://www.arcticwolf.com.
 C1Booth: 310
C1’s Cybersecurity Solutions deliver advanced protection across networks, users, applications, endpoints, and cloud environments. Designed to ease the burden on IT teams, our services simplify security management, enhance efficiency, and proactively defend against emerging threats, ensuring your enterprise remains resilient and secure. C1 collaborates with most of the Fortune 100 companies along with other key global industry partners to deliver solutions with a total lifecycle approach. C1 holds more than 5,600 technical certifications across thousands of engineers throughout North America, including three Customer Success Centers.
 Canary TrapBooth: 320
Canary Trap is a recognized industry leader in offensive security, security advisory and assessment services. Founded by ethical hackers and certified security experts who share in the common goal of protecting organizations from becoming a victim of the next cyber-attack.
Canary Trap combines human expertise with sophisticated tools and, where appropriate, threat intelligence to ensure a thorough, in-depth approach to all security testing and assessments.
 ClearVectorBooth: 110
ClearVector discovers and maps all activity to human, non-human, and third-party identities across your entire production environment—from the control plane to containers to serverless functions. Within 30 seconds to two minutes, you know exactly who did what, eliminating hours-long investigations. When risky activity is detected, ClearVector enables instant isolation of compromised identities, S3 buckets, Lambda functions, and other resources with a single click—without breaking your production environment. This surgical precision stops attacks in progress while you investigate, with easy rollback once verified. ClearVector provides a single timeline that threads together activity from GitHub, through CI/CD pipelines, to AWS or GCP control plane actions, and into runtime behavior inside EC2, Lambda, and containers. This unified view reveals the adversary in ways that traditional tools miss.
 Concentric AIBooth: 120
Concentric AI is intelligent data security made easy. Its Semantic Intelligence™ platform uses context-aware AI to discover sensitive data, monitor risks, automate remediation, simplify compliance, and accelerate investigations. It delivers smart, targeted protection by understanding how data is used, shared, and exposed. Concentric AI also offers managed services to keep security programs lean, scalable, and effective. This end-to-end platform protects data at rest, data in motion, and all the GenAI tools users interact with—so organizations can stay compliant, reduce exposure, and safeguard critical information wherever it lives and however it travels.
 Cloud Security Alliance Atlanta ChapterBooth: TBD
The Atlanta Chapter advances cloud and cybersecurity best practices across the Southeast. We host meetups, trainings, research collaborations, and leadership forums. Our mission is to connect people, share practical methods, and support careers in a rapidly changing cloud landscape.
 CodeIntegrity, Inc.Booth: 445
CodeIntegrity, Inc. is a San Francisco-based computer security startup founded in 2024 that provides secure runtime controls and guardrails for autonomous AI agents.
 Cyversity Atlanta ChapterBooth: TBD
Our mission is to achieve the consistent representation of women and underrepresented minorities in the cybersecurity industry through programs designed to diversify, educate, and empower. Cyversity tackles the “great cyber divide” with scholarship opportunities, diverse workforce development, innovative outreach, and mentoring programs.
 eSentire, IncBooth: 305
eSentire is the largest pure-play Managed Detection and Response (MDR) service provider, keeping organizations safe from constantly evolving cyber-attacks that technology alone cannot prevent. Its 24×7 Security Operations Center (SOC), staffed by elite security analysts, hunts, investigates, and responds in real-time to known and unknown threats before they become business-disrupting events. Protecting more than $6 trillion in corporate assets, eSentire absorbs the complexity of cybersecurity, delivering enterprise-grade protection and the ability to comply with growing regulatory requirements. For more information, visit www.eSentire.com and follow @eSentire on Twitter.
 Everpure, Inc. (formerly Pure Storage)Booth: 440
We are Everpure. We don’t just store data—we bring it to life.
As AI becomes core to business, infrastructure must evolve, yet too many organizations are still relying on rigid, siloed systems built for the past. The Everpure Platform replaces static storage with a unified, living platform that evolves with you—agile, resilient, and built to scale—so you can eliminate friction and unleash the power of your data.
 InfraGard Atlanta Members AllianceBooth: TBD
InfraGard Atlanta Members Alliance (IAMA) is a non-profit organization serving as a public-private partnership among U.S. Businesses, individuals involved in the protection and resilience of the U.S. critical Infrastructure and the Federal Bureau of Investigation.
InfraGard National Members Alliance (INMA), which consists of local InfraGard Members Alliances (IMAs) throughout the country. An InfraGard “chapter” refers to the local FBI, the local IMA, and the local InfraGard members working together.
IAMA is the Atlanta chapter of InfraGard. It is a local association of persons who represent businesses, academic institutions, state and local law enforcement agencies, non-profit organizations and other participants dedicated to sharing information and intelligence to prevent hostile acts against the United States.
 ISACA AtlantaBooth: TBD
The aim of the ISACA Atlanta Chapter is to sponsor local educational seminars and workshops, conduct regular chapter meetings, and help further promote and elevate the visibility of the IT audit, risk, control and security professions throughout the local area.
Nearing its 50th year, ISACA is a global association helping individuals and enterprises achieve the positive potential of technology. Today’s world is powered by technology, and ISACA equips professionals with the knowledge, credentials, education and community to advance their careers and transform their organizations. ISACA leverages the expertise of its half-million engaged professionals in information and cyber security, governance, assurance, risk and innovation, as well as its enterprise performance subsidiary, CMMI Institute, to help advance innovation through technology.
 ISC2 AtlantaBooth: TBD
ISC2 Atlanta chapter encompasses the Atlanta Metro area. Our chapter program provides members a forum to facilitate the exchange of knowledge and ideas, development of leadership and professional skills, and advancement of information systems security. We also provide our members with access to a variety of industry resource and educational programs to keep our members informed of the latest advances in technology and techniques.
Our mission is to advance information security in local communities throughout Atlanta, Georgia, by providing our members and other security professionals with the opportunity to share knowledge, grow professionally, educate others, and collaborate on projects.
 ISSA Metro Atlanta ChapterBooth: TBD
The ISSA Metro Atlanta chapter has developed over the years into one of the largest ISSA chapters worldwide and the largest IT Security organization in the Metro Atlanta area. The Information Systems Security Association (ISSA)® is a not-for-profit, international organization of information security professionals and practitioners. It provides educational forums, publications, and peer interaction opportunities that enhance the knowledge, skill, and professional growth of its members.
 KeysightBooth: 335
Keysight’s portfolio of network security solutions simulate threats, eliminate blind spots, taking control of a rapidly-changing attack surface. Be a hero, not a headline, by proving your network is secure simulating attacks, exposing gaps early, and course correct with step-by-step fixes; protecting users and applications with increased the efficiency, performance, and reliability of your security systems; patrolling every packet eliminating vulnerable blind spots and decrypt threats hiding in SSL traffic; and practice your cyber skills enhancing your security and attack response skills against real-world threats.
 Legit SecurityBooth: 300
Legit Security is a cyber security company offering a SaaS-based solution that secures an organization’s software supply chain to prevent sensitive data leaks and insecure software releases. Legit provides enterprise security leaders with the visibility and contextual information they need to minimize risk, and provides software development and DevOps leaders with tools to ensure their teams and build processes adhere to best practices. With Legit Security, your business can stay secure while releasing software fast.
Software supply chain attacks and security incidents involving the SDLC are growing rapidly, and can result in devastating damage including an unfortunate multiplier effect on downstream software consumers all with one attack. The team at Legit Security is on a mission to protect companies from this rapidly growing threat with a SaaS solution that supports both cloud and on-prem resources and is very easy to implement. Contact us to learn more about our solution and career opportunities at Legit.
 ManageEngineBooth: 205
ManageEngine crafts the industry’s broadest suite of IT management software. We have everything you need—more than 60+ enterprise products and 60+ free tools—to manage all of your IT operations, from networks and servers to applications, service desk, Active Directory, security, desktops, and mobile devices.
Since 2002, IT teams like yours have turned to us for affordable, feature-rich software that’s easy to use. You can find our on-premises and cloud solutions powering the IT of over 280,000 companies around the world, including nine of every ten Fortune 100 companies.
As you prepare for the IT management challenges ahead, we’ll lead the way with new solutions, contextual integrations, and other advances that can only come from a company singularly dedicated to its customers. And as a division of Zoho Corporation, we’ll continue pushing for the tight business-IT alignment you’ll need to seize opportunities in the future.
 MGT Impact SolutionsBooth: 330
MGT is a national technology and advisory solutions leader serving state, local government, education (SLED) and targeted commercial clients. Our specialized solutions solve the most critical issues that live at the top of our clients’ leadership agenda. We partner to help clients build resilience, implement systematic change and strengthen their foundations, now and for the future. MGT is committed to impacting communities for good. For more information, visit us at mgt.us.
 P0 SecurityBooth: 215
P0 Security is helping companies modernize PAM for multi-cloud and hybrid environments with the most agile way to ensure least-privileged, short-lived and auditable production access for users, NHIs and agents. Centralized governance, just-enough-privilege and just-in-time controls deliver secure access to production, as simply and scalably as possible. Every identity. Every system. All the time.
P0’s Access Graph and Identity DNA data layer make up the foundational architecture that powers privilege insights and access control across all identities, production resources and environments. With P0, production access is least-privilege, short-lived and auditable by default, including the new class of AI-driven agentic workloads emerging in modern environments.
To explore P0 Security further or book a demo, visit p0.dev.
 Seceon Inc.Booth: 430
Seceon delivers a next-generation cybersecurity platform that empowers enterprises, MSPs, and MSSPs to detect, respond, and remediate threats in real-time, eliminating the need for 20+ security tools.
What Sets Seceon Apart:
- Unified Platform: Combines SIEM, SOAR, UEBA, EDR, NDR, Threat Intelligence, Vulnerability Management, and Compliance into one AI-powered solution.
- AI-Powered Threat Detection & Auto-Response: Leverages ML, AI, and Dynamic Threat Models for real-time threat identification and automated remediation.
- Scalable & Multi-Tenant: Supports massive scale, processing 10M+ events per second, across enterprises and MSSPs from a single dashboard.
- Continuous Compliance: Streamlines security analytics and regulatory compliance (NIST, ISO, HIPAA, PCI-DSS, CMMC, NIS2) with aiSecurity360.
Why Organizations Choose Seceon:- Cut cybersecurity costs by 60% by replacing siloed tools
- Stop threats faster with AI-powered detection and automated response.
- Achieve full visibility by correlating real-time logs, flows, identities, for situational awareness and historical threat intelligence.
Faster protection, full visibility, and lower costs. Seceon powers the future of cybersecurity.
 SemperisBooth: 200
For security teams charged with defending hybrid and multi-cloud environments, Semperis ensures the integrity and availability of critical enterprise directory services at every step in the cyber kill chain and cuts recovery time by 90%. Purpose-built for securing hybrid Active Directory environments, Semperis’ patented technology protects more than 50 million identities from cyberattacks, data breaches, and operational errors. The world’s leading organizations trust Semperis to spot directory vulnerabilities, intercept cyberattacks in progress, and quickly recover from ransomware and other data integrity emergencies.
As part of its mission is to be a force for good, Semperis offers a variety of cyber community resources, including the award-winning Hybrid Identity Protection (HIP) Conference, HIP Podcast and free identity security tools Purple Knight and Forest Druid.
 Splunk, a Cisco CompanyBooth: 100
Splunk helps build a safer and more resilient digital world. Organizations trust Splunk to prevent security, infrastructure and application incidents from becoming major issues, absorb shocks from digital disruptions and accelerate digital transformation.
 StrongestLayerBooth: 210
Enhanced security in minutes and get immediately unparalleled protection. Our AI platform detects AI-driven and complex attacks missed by traditional tools, offering superior protection without complicated setup.
 TeramindBooth: 420
Founded in 2014, Teramind has become the global leader in behavioral solutions as over 10,000 organizations in 125+ countries, across every industry, have turned to Teramind to protect and optimize their business.
The power of Teramind is proven by its track record and has been recognized by numerous publications and industry analysts, including Forbes. ThreatLockerBooth: 340
ThreatLocker® is a global cybersecurity leader, providing enterprise-level cybersecurity tools to improve the security of servers and endpoints. ThreatLocker’s combined Application Whitelisting, Ringfencing™, Storage Control, and Privileged Access Management solutions are leading the cybersecurity market towards a more secure approach of blocking unknown application vulnerabilities. To learn more about ThreatLocker visit: www.threatlocker.com
 TorqBooth: 410
Torq is your security product’s favorite security product. Torq Hyperautomation unifies and automates the entire security infrastructure to deliver unparalleled protection and productivity.
 Trinity CyberBooth: 450
Trinity Cyber is an international cybersecurity firm that invents and operates innovative solutions to the most difficult cybersecurity challenges. The company’s products and services replace multiple market segments in the traditional cybersecurity market, with customers in over a dozen of the largest market verticals. The company’s founders, management team, and technologists are all award-winning, recognized leaders in their field—and their tech has revolutionized network security.
- Ahanu BoyleCyber Risk Analyst, Cyber Risk Opportunities LLC
Ahanu is a cyber risk analyst with Cyber Risk Opportunities who brings years of hands-on information security experience to the enterprise AI challenge. They lead cyber risk management initiatives for organizations of all sizes, translating complex security concepts into actionable strategies that business leaders can implement.
Since the emergence of generative AI, Ahanu has been at the forefront of enterprise AI security helping organizations safely integrate LLMs into their operations without sacrificing productivity or innovation. Their specialty lies in building secure AI workflows that actually work in practice, bridging the gap between cutting-edge technology and real-world business needs.
Ahanu’s approach centers on a core belief: effective security enables innovation rather than blocking it.
- Ricky SteeleChief Development Officer, TekStream; Author, "The Heart of Networking" (Third Edition)
Richard E. Steele, Jr., widely known as “Ricky,” is the Chief Development Officer at TekStream Solutions. TekStream provides IT staff augmentation and consulting services and was recently named one of Atlanta’s “Best Places to Work.” Steele has spent 20 years in the staffing industry successfully increasing revenue, elevating the company’s brand awareness, and expanding the customer base to include numerous Fortune 500 clients and start-ups. Steele’s prior work experience includes serving as a Client Partner at Korn Ferry, Director of Emerging Growth Technology Practice at PwC, and President of Cox Innovative Media. Steele is a ten-time entrepreneur and was honored as the “Georgia Small Businessperson of the Year” by the Small Business Administration in 1986.
Steele is a published author of three books, the most recent being "The Heart of Networking" (Third Edition). The principles from his book revolve around networking through “Servant Leadership and living the Golden Rule.” He has received numerous accolades for his authentic and heartfelt style as he has shared his in-depth knowledge in speaking engagements for companies, not-for-profits, faith-based organizations, and universities.
Steele has had a passion for serving the needs of his community and was recently honored by being inducted into the Martin Luther King, Jr. International Chapel Board of Sponsors, which recognizes individuals drawn from civic life, business, philanthropy, and organizational leadership who support the Chapel’s mission and the values Dr. King embodied. Steele was also awarded a “Lifetime Achievement” award by the “Aurora Day Camp,” which provides services for children with cancer, and the “Ann Cramer Volunteer of the Year” award from TechBridge for his service to the organization since its inception 25 years ago.
Steele was Co-Founder and the first Chairman for both Atlanta’s Table and Hospitality Helping Hands. He currently serves on The Carter Center Board of Councilors. He has also served on the Board of Trustees for Leadership Atlanta and The Ron Clark Academy. Mr. Steele is an Alumnus of Leadership Atlanta, Leadership Georgia, and Outstanding Atlanta. Steele's latest not-for-profit effort is Technology Cares/Technology Shares where over the past nine years, 1.4 million individual meals have been distributed to hungry Atlanta neighbors through The Atlanta Community Food Bank.
Steele is a native of Atlanta, and has been married to his wife, Beth, for 46 years. He is a proud father of three children and is a committed “Papa” to six cherished grandchildren.
- Mikal HassPresident, ISC2 Atlanta
Mikal is a 30-year information security, risk management, and IT professional with a strong background in development, architecture, and management. He has considerable expertise in designing, building, and managing information security and risk management programs in highly-regulated private and public sector organizations.
- Michael MarsilioCISO, Information Security & Compliance Officer, Paradies Lagardère
Michael Marsilio is the Information Security and Compliance Officer for Paradies Lagardère, where he is responsible for information security, risk management, privacy, and compliance. Michael plays a strategic role in protecting Paradies Lagardère computing environment and data, he also helps drive global security initiatives. He has more than 30 years of experience in building and managing security and compliance programs for both public and private companies and has a substantial track record in PCI, PII, PHI, IT General Controls and developing cybersecurity policy for financial, retail, and legal organizations.
He is based at Paradies Lagardère Corporate Headquarters, in Atlanta, GA.
- Tamika BassCybersecurity Director, GFT
Tamika Bass is an Information Security professional with more than 17 years’ experience in information security, including information security governance and risk management. Tamika is passionate about improving communication and understanding of information security in the industry. Tamika is an active speaker, college professor and enjoys spending her time educating technical staff on the importance of communicating effectively in the Information Technology space. Tamika holds the following certifications: CISA,CRISC, HCISPP, CBCP.
- Jeremy KoppenEVP, CISO, Equifax
Jeremy Koppen is Chief Information Security Officer of Equifax, charged with continuing the company’s leadership in security, a core component of the Equifax EFX2027 Strategic Priorities.
Prior to joining Equifax, Jeremy served as Managing Director of Mandiant, part of Google Cloud, where he led hundreds of cyber engagements for Fortune 100 and 500 companies with a focus on mitigating emerging threats, scaling security operations through automation and AI, and enhancing cyber resilience. Jeremy has provided strategic counsel to government leaders, corporate boards, and C-Suite executives, and has played a key role in responding to some of the most advanced cybersecurity threats across industries.
Jeremy holds a bachelor’s degree in Computer Science from the University of Iowa and a master’s degree in Computer Science with a concentration in Digital Forensics from the University of Rhode Island.
- Jim BalloweCISO / CIO, Esquire Deposition Solutions, LLC
- Steven TepplerPartner & Chief Cybersecurity Legal Officer (CCLO), Mandelbaum Barrett PC
Steven is Mandelbaum Barrett’s Chief Cybersecurity/Legal Officer. An ISACA Certified Data Privacy Solutions Engineer, Steven’s client-facing practice focus is on cybersecurity and privacy, risk assessments and data breach response, AI risk, and regulatory compliance. He regularly publishes on cybersecurity law, privacy, and emerging technology risk, advises organizations on aligning technical security programs with legal and regulatory obligations, and teaches Cybersecurity Law at Nova Southeastern University Law School.
- Jennifer BollingRegional Director, Cyber/Professional Liability - Midsouth Region, USI Insurance
Jennifer Bolling is a Regional Cyber Director for the Executive & Professional Risk Solutions (EPS) Practice within the Midsouth Region and is based out of the Atlanta, GA office. Jennifer specializes in consulting and broking services for Cyber and Professional Liability and her responsibilities include assessment of exposures, coverage and program structure, strategic action planning, market negotiation and program placement. Jennifer’s 21+ years of insurance industry experience enables her to take an enterprise view of risk across all professional risk lines.
Before joining USI in 2021, she was with Arthur J Gallagher & Co. for nearly 17 years as a Senior Resource Specialist focusing on Management and Cyber Liability. Jennifer has placed management and professional liability coverages and related lines for a variety of organizations, including large publicly traded, privately held and not-for-profit entities in various industries. Prior to Gallagher, Jennifer’s work included marketing and business development for software companies.Jennifer earned a BBA degree from Mercer University – Stetson School of Economics, Macon, GA and was also a Tift College Scholar. She earned her Cyber COPE® Insurance Certification℠ (CCIC) which is an eight-month program developed and delivered by Chubb and Carnegie Mellon University’s Heinz College of Policy & Information Systems.
She is a member of Professional Liability Underwriting Society and Women in CyberSecurity (WiCyS), and a winner for Risk & Insurance 2021 Power Broker (Cyber category).
Jennifer grew up in Buford, GA, and currently resides in Birmingham, AL.
- April SolanoSoutheast Regional Cyber Manager, Bowhead Specialty
- Dr. Erika VossSVP, Global Chief Security Officer, Blue Yonder
Strategic security executive with over two decades of transformational leadership across the world's most demanding technology and enterprise environments. Proven track record driving enterprise-wide security strategies that align with business objectives while managing complex, global teams and regulatory compliance frameworks. Recognized expert in designing and implementing comprehensive security architectures that enable digital transformation while maintaining the highest standards of protection across application security, infrastructure security, cloud security, identity and access management, third-party risk, and enterprise threat detection.
In her current role as SVP, Global Chief Security Officer at Blue Yonder, a leading provider of end-to-end supply chain software and solutions for global enterprises, Dr. Voss sets strategic direction and drives execution across all facets of the organization's security program. Leading a high-performing team of security engineers, architects, and security operations experts, she establishes security policies, procedures, and practices that protect enterprise assets while enabling business velocity and innovation. Her responsibilities encompass application security, infrastructure security, access control and identity management, third-party risk management, threat detection and response, and regulatory compliance for complex global supply chains.
Drawing on her extensive tenure at industry-leading organizations including Amazon Web Services, Microsoft Corporation, Oracle Public Cloud, Salesforce, and Capital One, Dr. Voss has consistently delivered transformational security programs that reduce risk, enhance operational resilience, and support scalable growth. Her expertise spans foundational security architecture, fraud detection and prevention, identity management, and enterprise cloud security practices.
- Kelly WilhoitSr. Director of Treasury, Blue Yonder
- Lucas PersellSr. Solutions Architect, C1
Lucas brings more than a decade of cybersecurity expertise to the C1 team, specializing in creating outcome-based security roadmaps for complex enterprise environments. With a background spanning systems engineering at Cisco and cloud architecture, he excels at bridging the gap between technical defense and business risk. Lucas is dedicated to helping clients navigate the evolving threat landscape through strategic design, zero-trust frameworks, and a relentless focus on long-term security resilience.
- Damian AponeGlobal Director, Governance, Risk & Compliance, Genuine Parts Company
- Dinesh BabuAssociate Director of Enterprise Business Support for Americas, ManageEngine
At ManageEngine, leadership in enterprise support for the Americas encapsulates my commitment to advancing Endpoint Management & Security. Our team's dedication to empowering customers with cutting-edge solutions has solidified our role as industry pace-setters. My tenure at Zoho Corporation, spanning roles from Regional Technical Account Manager to Associate Director, has been marked by fostering robust customer relationships and spearheading technical innovation. With skills honed in system administration and mobile device management, I contribute to the seamless integration of ManageEngine products, ensuring exceptional service delivery.
- Chris BellVP of Strategic Accounts, Seceon
IT and managed security sales specialist with over fifteen years of experience. Proficient at gathering business requirements, analyzing business needs, and presenting technology strategies and solutions that align with business objectives. My main goal is to help the enterprise increase user productivity, decrease risk and control costs.
Specialties: Cybersecurity, EDR, MDR and XDR services, Managed aiSIEM, Penetration Testing & Vulnerability Assessment, Managed IT Services, Virtualization, Data Storage and Protection, Data Center Solutions, Disaster Recovery Expertise and Network Infrastructure Solutions.
- Michael GutscheSecurity Advisory Lead, Splunk, a Cisco Company
Michael Gutsche is a security expert recently promoted to run the Security Advisory Team for North America. In this role, Mr. Gutsche is responsible for running a team of exports that help drive security strategies for our largest customers. Michael joined Splunk with over 25 years of experience building large enterprise security and operations programs. Most recently he was Chief Cyber Security Strategist for HPE. However, he has spent most of his 25+ year career on the practitioner side. Prior to HPE he held leadership positions of Senior Vice President of Core Operations at Mastercard International, and Chief Information Security Officer at Sisters of Mercy Health System and Express Scripts.
- Dave HowellChief Marketing Officer, Legit Security
Dave leads all aspects of marketing including brand positioning, demand generation, and product marketing. Before Legit, Dave was CMO at ThreatX, an API and app protection platform. Previously, Dave led marketing teams at ZeroNorth, Forcepoint, Raytheon, and RSA Security. In his free time, Dave enjoys live music, CompTrain, yoga, and spending time with his wife and three children.
- Phillip MahanSr. Director, Privacy & Compliance, GoTo Foods
The boring Bio for Phillip would mention his years of experience in Privacy, Security, Governance, and Audit. It would tell of the business sectors he's worked with, and perhaps even the companies and professional organizations he's been affiliated with for the last 25+ years.
This is not that Bio.
Telling stories and pulling connections together from places unexpected; using Poetry, Literature, and Fairy Tales to make points understood by those not in the tech field; and sometimes writing way too strange abstracts—these are the things that make Phillip happy.
When a group wants him to come up with a talk, his wheels start turning and they don't stop until something is on paper (or on a screen ). The results are usually a journey that leave the listeners somewhere they weren't when the story began.
Phillip prefers people thinking of him more as someone who looks at the world differently but helps to get you where you need to be.
- James AzarCISO, Artera Services
- Jim DoggettCISO, Semperis
James (Jim) is a veteran in the information security and risk space. He previously served as partner at Ernst & Young, where he helped build the company’s cybersecurity practice during his 27-year tenure. Most recently, Jim worked as CISO and head of US operations at Panaseer. He has also held positions as CTRO at AIG, CSO and CTRO at Kaiser Permanente, and managing director at JP Morgan Chase, where he was global leader of Information Risk and Resiliency, Treasury and Security Services.
- Jordanne BarrettBISO, AT&T
- Katherine CollinsBISO, Boston Consulting Group
- Shu BouissetBISO, NCR Voyix
- Robert LeeBISO, Deluxe
- Cassandra DacusPresident, Cyversity Atlanta Chapter
- Alan LeFortCEO & Co-Founder, StrongestLayer
Alan brings 25 years of cybersecurity leadership spanning enterprise B2B and B2B2C markets. Before founding StrongestLayer, he held senior roles at Proofpoint, McAfee, Intel Security, and HyTrust, focused on advanced threat protection, insider risk management, and behavioral analytics. At Intel Security he directed global product strategy across EMEA, leading teams in the U.S., Europe, and Israel. He holds a BBA in Finance from the University of St. Michael's College and completed his Executive MBA in Leadership, Strategy, and Design Thinking at Rotman School of Management. Alan joined StrongestLayer as CEO in early 2025 after advising the founding team, recognizing the strategic opportunity: if only AI can defend against weaponized AI, reasoning-based detection becomes essential.
- Jason PayneSales Engineer, Torq
Jason Payne is a Sales Engineer at Torq, where he helps security teams modernize the SOC with AI-driven automation. He brings roughly two decades in cybersecurity, with a career that runs from the analyst's seat to the operations leadership chair. Jason spent nearly a decade leading security operations as a Senior Director, running a 24/7 MDR SOC, before moving into solutions engineering and security architecture. His earliest work was decidedly hands-on, from deploying intrusion detection and cleaning up compromised hosts to building the monitoring systems behind a rapidly scaling platform. That operator's background is the through-line: Jason has triaged the incidents, led the teams that live in the queue, and now focuses on how AI can carry that load without adding risk. He is based in Houston, Texas.
- Scott TaylorDirector of Cyber Resilience, Field Solution Architects, Everpure
Scott Taylor is a senior technology leader with over 23 years of experience across end-user, partner, and manufacturer environments within the IT industry. He currently serves as Director, Cyber Resilience, Field Solutions Architect at Everpure, where he leads technical strategy and helps drive customer success through innovative security and resilience solutions. For more than a decade, Scott has focused on pre-sales technical leadership, building and guiding high-performing teams that consistently deliver measurable business outcomes.
He is passionate about delivering innovative and efficient solutions while fostering a growth-oriented culture grounded in strategic thinking and strong leadership. Throughout his career, Scott has successfully navigated complex technical landscapes, providing valuable insights to clients, executive leadership, and key stakeholders. Known for cultivating high-performing, collaborative teams across practices and business units, he promotes continuous learning, creativity, and a strong focus on helping clients achieve their business objectives.
- Chamon GaytonSenior Associate, Schellman; Co-Founder, Ethics Security
Chamon Gayton is a highly motivated and accomplished cybersecurity professional and retired military veteran, bringing over 17 years of proven experience in security operations, governance, risk and compliance (GRC), and information assurance within both federal and private sector environments. Specializing in leading enterprise-wide security initiatives, Chamon has a distinguished record of successfully guiding organizations through complex compliance and security challenges, with deep expertise in federal frameworks including FISMA, FedRAMP, StateRAMP, NIST (800-53, 800-53A, 800-18, 800-60), FIPS 199 & 200, and DoD standards.
Throughout her career, Chamon has demonstrated a consistent ability to build and lead high-performing cybersecurity teams, while developing cross-functional programs from initial planning through implementation — mitigating risk, ensuring compliance, and delivering strong internal and customer-facing outcomes. Her leadership style emphasizes strategic collaboration, continuous improvement, and mission-focused execution.
With a sharp analytical mindset and strong data analysis capabilities, Chamon excels at identifying and addressing security vulnerabilities, synthesizing large datasets to drive decision-making, and enhancing long-term security postures. She has successfully performed and overseen numerous security assessments, audits, and readiness reviews, ensuring adherence to critical state, federal, and industry regulations.
Drawing on her military discipline and leadership acumen, Chamon is known for her ability to mentor emerging security professionals, establish trusted relationships across technical and executive teams, and cultivate a security-first culture. Her hands-on approach and clear communication style make her a valuable contributor to any initiative aimed at elevating security maturity and resilience.
Chamon holds multiple industry certifications and continues to stay at the forefront of evolving cyber threats, emerging regulations, and risk management strategies. Whether advising senior leadership or leading tactical execution, she brings both vision and operational excellence to every engagement.
- John LaliberteCEO, ClearVector
John Laliberte is the CEO and founder of ClearVector, a leading provider of real-time, identity-driven security for production environments. John has more than 18 years of cybersecurity experience. Prior to ClearVector, John served as SVP/CTO at FireEye/Mandiant, responsible for the global business unit encompassing endpoint security product, email security (cloud) product, cloud and data center operations, data science, and advanced R&D. Prior to joining Mandiant in 2008, John served at the NSA, where he was responsible for research and development. John holds a master's degree in Computer Science and a bachelor's degree in Physics and Astronomy from Boston University.
- Joseph BlankenshipVP, Research Director, Forrester Research
Joseph supports security and risk (S&R) leaders, helping clients develop security strategies and make informed cybersecurity decisions. As a research director, he leads the analyst team researching security leadership, the role of the CISO, detection and response, and Forrester’s Zero Trust model. His research focuses on insider risk management, security operations, and security management. His over 20 years of security experience includes roles at Solutionary, McAfee, Vigilar, and IBM (ISS), where he focused on managed security and consulting services, email security, network security, and compliance. Joseph holds an MBA from Kennesaw State University and a BA from Auburn University.
- Jeremy GudgelSecurity Technology Strategy Director, Akamai
Information technology leader and experienced practitioner with exposure in delivery of Cyber Risk Management for a number of regional, national, and global organizations. Former Accountable Officer, proven ability to direct mitigation of risk and implement frameworks/controls that align with organizational goals and comply with regulations in Companies listed on the Stock exchange. Skilled in leading teams, departments, and 24x7 operations to ensure support, leading cyber investigations, safety of company data, and high availability of systems and processes.
- Chris LariscyPrincipal Solutions Architect, MGT
Christopher Lariscy, CISSP, GCIH, is a Principal Solutions Architect with MGT Impact Solutions, Technology Solutions Group. He has 21 years in information technology and has been security-focused since 2010, working with K-12, higher education, state and local government, healthcare, and commercial clients. His practice covers security architecture, assessment against NIST and CIS frameworks, incident response, tabletop exercise design and facilitation, AI governance, and virtual CISO advisory. He authored MGT's K-12 guidance on agentic AI and AI-assisted learning, covering both the controls that govern district AI use and the ways attackers use AI against them, and he writes and speaks on AI governance and federal AI policy. He holds a Bachelor of Science in Computer Science from Georgia Southern University and is completing a Master of Science in Cybersecurity at the Georgia Institute of Technology.
- Jacob ProsserDirector, Detection Engineering, Cox Automotive
Jacob Prosser is a seasoned cybersecurity professional with more than 14 years of experience in the field. As a Director of Cyber Defense at Cox Communications, he and his team play a critical role in keeping the company and its customers safe from cyber threats. His expertise spans various domains within cybersecurity including application security, identity and access management, security architecture, detection engineering, and incident response.
Jacob graduated from the University of Georgia with a degree in Management Information Systems, and he holds a CISSP certification.
- Steve HodgesState CISO, State of Georgia
Steve Hodges is the State Chief Information Security Officer for the State of Georgia, where he leads enterprise cybersecurity strategy, governance, operations, and modernization across a large and complex public-sector environment.
Steve has spent more than 30 years working across technology, operations, and cybersecurity. His career began close to the technology—with programming, databases, networks, infrastructure, and operations—and later evolved through enterprise architecture, business continuity, disaster recovery, governance, risk, and cybersecurity leadership. That experience has shaped how he thinks about security today.
Steve understands what happens when a security decision reaches the operational environment. His work increasingly focuses on the organizational challenges that determine whether an enterprise can act when time matters: trust, decision rights, relationships across organizational boundaries, and the ability to move from information to decision to action.
He speaks and writes about cybersecurity leadership, enterprise resilience, decision velocity, trust, governance, organizational transformation, and emerging technology. His recent work explores Continuous Incident Response and the need to build the trust, authority, and alignment required to act before an incident begins—not try to assemble them after an attacker is already moving.
Steve is a frequent speaker at cybersecurity, technology, and executive leadership events, including SecureWorld, Info-Tech LIVE, AWS Public Sector Innovation Day, StateScoop’s Cybersecurity Modernization Summit, the Georgia Digital Government Summit, and other industry and government forums.
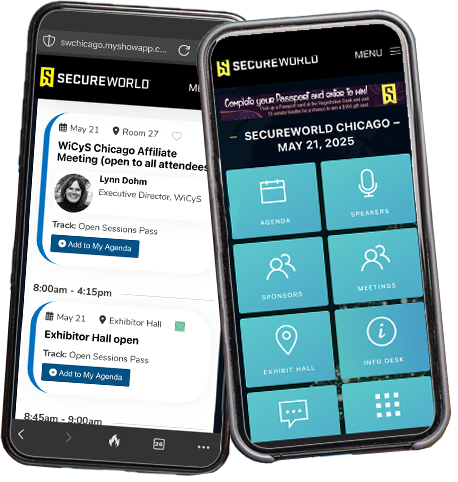
Easily navigate your conference experience and make the most of your day with a dedicated conference app!
- Streamline event check-in
- Discover relevant topics and speakers
- Find your way with interactive venue maps
- Connect with fellow attendees
- View speaker presentation slides (post-event)
- Download a Certificate of Attendance
Hone your skills and connect with your regional peers in InfoSec.
