SecureWorld conferences blend world-class keynotes, breakout sessions, small group discussions, and opportunities to earn CPE credits.
 Open Sessions
 Conference Pass
 SecureWorld Plus
 VIP / Exclusive
- Wednesday, November 18, 20268:30 amExhibitor Hall openRegistration Level:
- Open Sessions
8:30 am - 3:00 pmLocation / Room: Exhibitor HallYour opportunity to visit our solution vendor partners, whose sponsorship makes SecureWorld possible! Peruse the many downloadable resources each booth has to offer.
9:00 amOPENING KEYNOTERegistration Level:- Open Sessions
9:00 am - 9:45 am9:45 amNetworking BreakRegistration Level:- Open Sessions
9:45 am - 10:00 amLocation / Room: Exhibitor HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
10:00 amAI vs. AI: Securing the Agentic Enterprise Against Automated Threats Enterprise IT - Sr. Solution Architect, AssurantRegistration Level:
- Open Sessions
10:00 am - 10:45 amAs enterprises move from experimenting with AI to deploying autonomous agents in production, the attack surface is changing just as fast as the defenses. When ransomware hit MGM Resorts in 2023, it knocked out reservations, room keys, and slot machines for over 10 days a warning sign that manual, rule-based security can’t keep pace with modern, AI-accelerated attacks. This session covers how machine learning detects anomalies and automates threat response in real time, how attackers are using generative AI for smarter phishing and social engineering, and how organizations can build responsible-AI guardrails governance, model evaluation, human oversight into agentic systems from day one, so speed doesn’t come at the cost of safety.
Key takeaways:
Attendees will leave with a practical framework for applying AI and machine learning to real-time threat detection and automated response plus a clear-eyed view of how attackers are using generative AI against them. Most importantly, they’ll understand how to adopt AI-driven security responsibly, pairing automation with governance, model evaluation, and human oversight so speed doesn’t come at the cost of accountability.
10:00 amA Spy's View on Indicators of Insider Threats Founder & CEO, VigilanceRegistration Level:
- Open Sessions
10:00 am - 10:45 amDuring this session, the audience will hear from a former CIA Operations Officer who spent a career creating and exploiting insider threats in the hardest target countries and companies. He will describe common detectable activities that malicious insiders conduct inside a company that could lead to detection. The presentation will include facts about insider threats as well as case studies from the presenter’s time leading the Insider Threat program at Tesla. Attendees will walk away with concrete behaviors to look for when monitoring their computer networks and employee activity for indications of insider threat.
10:00 amFour Points of Exposure. Zero Room for AssumptionsHow IEEE 2883.1 Protects Data Across the Asset Lifecycle Sr. Content Strategist, Blancco Technology Group
 VP & GM, International Sales, Blancco Technology GroupRegistration Level:
- Open Sessions
10:00 am - 10:45 amMost enterprises have a policy for retiring devices, but far fewer address the other moments when stored data is at risk. In this session, Blancco experts break down IEEE 2883.1-2025, the new guidance on storage sanitization, and its four points of exposure across the asset lifecycle: provisioning, internal reuse, external reuse or resale, and disposal. You’ll learn the specific threats at each stage, including pre-installed malware and pre-harvested encryption keys.
You’ll also see how to choose between Clear, Purge, and Destruct based on data sensitivity and lifecycle stage, and where “verified” sanitization has real limits, especially cryptographic erase, and what that means for your audit trail. Finally, you’ll walk away with a best-practice framework for automating and centralizing sanitization across end-user compute and data center storage before devices leave your control.
10:45 amNetworking BreakRegistration Level:- Open Sessions
10:45 am - 11:00 amVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
11:00 amSignal Hijacked: How Mobile Networks Became Phishing's Most Trusted Delivery Layer Security Engineer, ConfidentialRegistration Level:
- Open Sessions
11:00 am - 11:45 amQR code phishing (quishing) is one of the fastest-growing threats in mobile security, yet remains completely invisible to carrier defenses. This talk presents original research introducing the Signal Switch—a measurable behavioral framework defining the moment a mobile user shifts from skepticism to compliance when faced with a QR-based attack delivered through a trusted mobile channel.
Real-world study: 55 participants, 190 live QR code scans across four scenarios (restaurant, parking, Wi-Fi, banking) deployed via WhatsApp and SMS with no warning. Key finding: 85% of participants scanned when delivered via mobile versus 49% who said they would in a survey. Zero hesitations. Zero questions asked.
The talk includes: a live audience demo where attendees scan a real QR code and experience the Signal Switch firsthand, AI detection comparison across Claude, ChatGPT, and Gemini, and a proposed carrier-layer intervention architecture for pre-delivery QR threat analysis—now subject to a pending patent application filed through Charter Communications.
11:00 amBuilding Incident Response Plans for Highly Distributed WorkforcesRegistration Level:- Open Sessions
11:00 am - 11:45 amSession details to come.
11:00 amFrom Alert Fatigue to Adaptive Defense: Operationalizing AI in the SOCRegistration Level:- Open Sessions
11:00 am - 11:45 amSession details to come.
11:45 amNetworking BreakRegistration Level:- Open Sessions
11:45 am - 12:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
12:00 pmThe Deepfake Coverage Gap: Is Your Cyber Insurance Keeping Up? Director of Information Security & Regulatory Compliance, ETSRegistration Level:
- Open Sessions
12:00 pm - 12:45 pmWhat happens when an employee follows instructions from a trusted executive, transfers millions of dollars, and later discovers the executive was an AI-generated deepfake? The financial loss is real. The identity was fabricated. But will the organization’s cyber insurance respond?
AI-powered impersonation challenges long-standing assumptions about fraud, identity verification, and insurable cyber risk. As deepfake-enabled social engineering becomes more convincing, insurers are reassessing how their policies address financial fraud, reputational damage, and incidents that occur without a traditional network compromise.
This session examines how the cyber insurance industry is responding to AI-driven deception, including emerging deepfake endorsements, affirmative AI coverage, exclusions, and the potential gaps between cyber and crime insurance.
Drawing on real-world incidents and emerging insurance industry practices, we’ll explore what cybersecurity leaders need to understand about their organization’s financial exposure—and why security controls, insurance coverage, and executive decision-making must evolve together.
Attendees will leave understanding:
- How AI deepfakes are changing the cyber insurance industry’s approach to social engineering and financial fraud
- Where traditional cyber insurance and commercial crime policies may leave organizations exposed
- What security and risk leaders should examine when evaluating insurance coverage for AI-enabled deception
12:00 pmYour Internal AI – Part II Sr. Director, Cyber Security, Acumatica, Inc.Registration Level:
- Open Sessions
12:00 pm - 12:45 pmThe enterprise AI landscape has matured rapidly, shifting the conversation from initial curiosity to operational reality. Yet as large language models (LLMs) weave deeper into daily workflows, they quietly amplify a critical vulnerability: the well-intentioned insider who inadvertently leaks confidential data to mainstream AI tools.
Serving as the next evolution of our discussion on generative AI governance—fully designed as a standalone briefing for first-time attendees—this session tackles how to balance aggressive productivity gains with ironclad security. The path forward is not restricting access, but establishing an enterprise-controlled gateway.
We will introduce “Your Internal AI,” a secure, scalable architecture that lets teams interact with modern LLMs naturally while ensuring confidential information never leaves organizational boundaries. Through dynamic pre-processing, anonymization, and inline policy enforcement, enterprise data remains protected at the edge.
Attendees will explore:
- How unsanctioned and mainstream AI usage expands the non-malicious insider attack surface
- The regulatory, privacy, and intellectual property stakes facing organizations today
- A live technical demonstration showing real-time prompt sanitation in active business workflows
- Frameworks for transforming security from an AI roadblock into a strategic enabler
12:00 pm[Panel] The Current Threat LandscapeRegistration Level:- Open Sessions
12:00 pm - 12:45 pmThe enterprise attack surface is no longer confined to traditional networks—it extends across distributed cloud environments, collaboration pipelines, identity fabrics, and decommissioned assets. As adversaries adopt automated tooling, sophisticated social engineering, and targeted data extortion models, security teams must evolve beyond reactive posture management to continuous, lifecycle-wide defense.
This panel brings together industry specialists to dissect the current threat landscape through the core technological capabilities driving real-world resilience:
- Hyperscale Threat Intelligence & Cloud Infrastructure Defense: How global telemetry, front-line frontline threat intelligence, and planetary-scale cloud infrastructure models uncover advanced persistent threats (APTs) and zero-day campaigns before they proliferate.
- Zero Trust Architecture & Secure Access Service Edge (SASE): Replacing perimeter trust models with identity-centric, least-privilege brokering and inline traffic inspection to halt lateral movement and secure hybrid workforces.
- Next-Gen SIEM & Unified Telemetry Analytics: Leveraging cloud-native log ingestion, real-time analytics, and automated alert correlation to dramatically shorten dwell times and triage alert fatigue in high-volume SOC environments.
- Programmable, AI-Driven Email & Inbound Threat Defense: Countering credential harvesting, business email compromise (BEC), and QR-code/quishing attacks with behavioral detection engineering and dynamic inspection layers.
- Defensible Data Lifecycle & Certified Sanitization: Eliminating data liability and residual exposure by operationalizing verified, policy-driven data erasure across active storage, virtual machines, and decommissioned endpoints.
Attendees will walk away with an integrated perspective on how to align proactive detection, inline Zero Trust controls, deep telemetry, and end-of-life data governance into an adaptable defense strategy.
12:45 pmNetworking BreakRegistration Level:- Open Sessions
12:45 pm - 1:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
1:00 pmOperationalizing Privacy: The Phased Playbook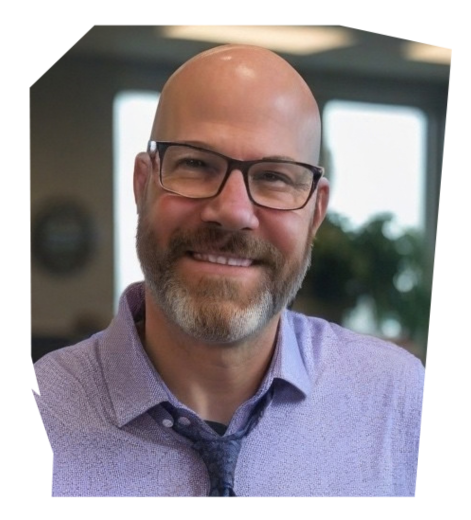 Executive Director of Cybersecurity & Infrastructure, Focus on the FamilyRegistration Level:
- Open Sessions
1:00 pm - 1:45 pmAs U.S. state privacy laws expand, organizations need practical, scalable ways to fulfill consumer privacy requests across complex data environments.
This session shares Focus on the Family’s phased approach to operationalizing privacy rights. We began with a manual, cross-functional process to establish accountability, understand data locations, and validate workflows. We then used existing Microsoft investments, e.g. SharePoint and Power Automate, to streamline request tracking, internal notifications, assignments, and administrative tasks.
As the program matured, we adopted DataGrail to automate request intake and fulfillment workflows across structured PII systems such as Salesforce and unstructured repositories such as Box. Attendees will learn how to build a privacy-request program incrementally, identify high-value automation opportunities, and balance existing tools with purpose-built privacy technology.
1:00 pmCyber Intel Debrief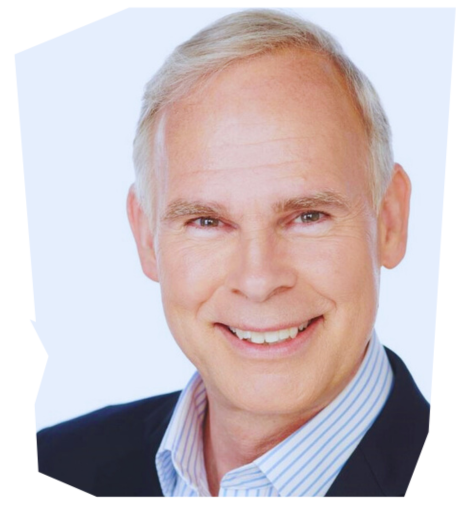 CNN Military Analyst; U.S. Air Force (Ret.); Founder & President, Cedric Leighton Associates, LLC
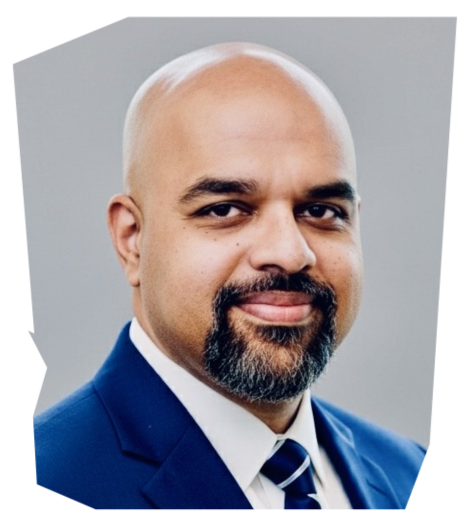 Founding Partner, CYFORIX (Former CISO & Sr. Executive at Keurig Dr Pepper, Comcast, HD Supply, and GE)Registration Level:
- Open Sessions
1:00 pm - 1:45 pmEnterprise security is no longer just a technical discipline; it is the primary battlefield of modern conflict. This session connects the dots between global geopolitical volatility and the immediate risks to organizational integrity, supply chain continuity, and stakeholder trust. We will examine how shifting alliances and conflicts involving major global powers are reshaping the cyber threat landscape—specifically targeting critical infrastructure, distributed cloud dependencies, and the global software supply chain.
The discussion will pivot to the “internal” evolution of the enterprise, analyzing the rapid integration of Generative AI into core business logic and automated decision-making systems, and the resulting regulatory and privacy minefield. From state-aligned actors seeking to destabilize national interests to sophisticated ransomware syndicates targeting high-availability environments, we will profile the adversaries threatening the modern digital order.
Join us for a 2026 outlook that moves beyond mere framework compliance, offering a battle-tested roadmap for maintaining operational resilience and data sovereignty in the face of unprecedented global instability.
1:00 pmTop Human Skills for Cybersecurity in the Age of AI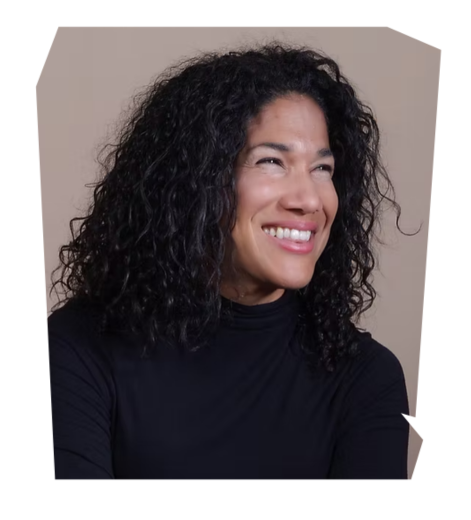 Founder, Hardcore Soft SkillsRegistration Level:
- Open Sessions
1:00 pm - 1:45 pmArtificial intelligence is changing the way we work, yet it isn’t replacing the need for humans to work well with humans. In this engaging and practical session, Yadi Caro challenges the idea that “soft skills” are simply nice-to-have traits. Skills like connecting, communicating, collaborating, creating, and navigating feedback and conflict are becoming essential to how teams perform, innovate, and adapt. Drawing on lessons from unexpected places, Yadi reveals what it really takes for people to work together when the environment is unpredictable, and constantly changing.
Benefits: Attendees will discover how to strengthen the distinctly human skills that AI can’t replace. They will learn how to work more effectively with their human colleagues.
1:00 pmControlling Your Security Data: Ingestion Cost, Compliance, and Federated SIEM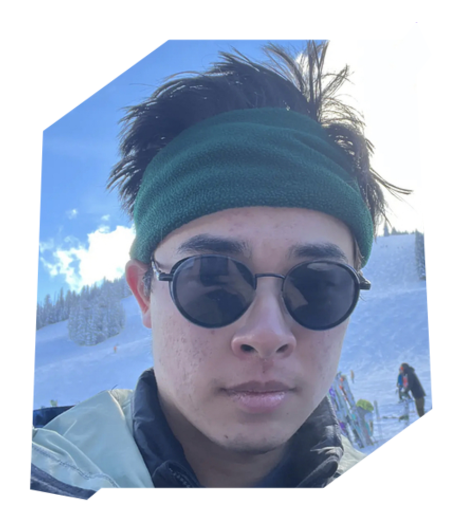 Product Manager, DatadogRegistration Level:
- Open Sessions
1:00 pm - 1:45 pmSecurity data volume is growing faster than SIEM budgets. Leading security organizations are taking control of their security telemetry before it hits the SIEM by managing SIEM ingestion cost, routing security data to multiple destinations and keeping analytics compliance-safe by scrubbing sensitive data before it leaves your environment.
In this session, we’ll share how to:
- Cut ingestion cost, not detection coverage: send critical security logs to your SIEM and route the rest to your data lake or archive at a fraction of the cost.
- Keep sensitive data in your environment: redact PII before logs leave your infrastructure, so analytics stay compliance-safe wherever the data lands.
- Write a detection once, let it work everywhere: normalize every source to OCSF, and see where federated SIEM takes detection next
Attendees will gain a practical approach on shrinking costs and widening what you’re able to detect.
1:45 pmNetworking BreakRegistration Level:- Open Sessions
1:45 pm - 2:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
2:00 pmCLOSING KEYNOTERegistration Level:- Open Sessions
2:00 pm - 2:45 pm

 Blancco Technology GroupBooth: TBD
Blancco Technology Group is the global industry standard in software-based data sanitization, secure data erasure, and mobile device diagnostics. Rather than physically destroying hard drives, servers, or mobile devices, Blancco permanently overrides the data so it cannot be recovered. This allows organizations to safely reuse, resell, or recycle their IT assets while complying with strict data privacy laws.
 Datadog
 is the essential monitoring platform for cloud applications. We bring together data from servers, containers, databases, and third-party services to make your stack entirely observable. These capabilities help DevOps teams avoid downtime, resolve performance issues, and ensure customers are getting the best user experience.
 Google Cloud Security
 provides organizations with leading infrastructure, platform capabilities and industry solutions to help them solve their most critical business problems. Google Cloud Security helps customers protect their global operations with solutions such as zero trust security, application and data protection, fraud prevention, and threat detection and response.
 Sublime Security
Sublime is the new standard for email security. Not just another black box, our AI-powered detection engine detects and prevents email attacks, so security teams can spend less time on email-originated incidents.
 Sumo Logic
 was founded in 2010 by experts in log management, scalable systems, big data, and security. Today, our purpose-built, cloud-native service analyzes more than 100 petabytes of data, more than 16 million searches, and delivers 10s of millions of insights daily – positioning Sumo among the most powerful machine data analytics services in the world.
 Strike48
’s core mission is to help you automate the extraction of business value from server logs. The Strike48 Prospector Studio is an AI Agent Creation and Management Suite that allows you to quickly start inspecting logs with AI agents. Use our Agent creation personas to help create Agents for your purposes or you can use our professionally pre-made Agents instead!
 Zscaler
 is universally recognized as the leader in zero trust. Leveraging the largest security cloud on the planet, Zscaler anticipates, secures, and simplifies the experience of doing business for the world’s most established companies.
- Animesh KumarEnterprise IT - Sr. Solution Architect, Assurant
Animesh Kumar is a Senior Solution Architect with 24+ years of experience designing secure, scalable, cloud-native enterprise solutions. He specializes in Enterprise AI, Generative AI, and multi-cloud architecture across Azure and AWS. Currently at Assurant, he provides architectural leadership across global business and product teams, with prior senior roles at Fiserv, American Airlines, and IBM. His expertise spans Azure OpenAI, RAG, LLMs, Kubernetes, DevSecOps, and Responsible AI governance. He holds a Master's in Computer Science from the Illinois Institute of Technology.
- Charles FinfrockFounder & CEO, Vigilance
Charles Finfrock is the Founder and CEO of Vigilance, a private intelligence and investigations firm based in Lexington, Kentucky. His background spans intelligence operations, corporate security, insider threat, counterintelligence, cybersecurity, cryptocurrency and financial crime, and open-source intelligence.
Prior to founding Vigilance, Charles developed and led Tesla’s Insider Threat Program and Global Information Security Investigations Team, overseeing efforts to protect sensitive information and intellectual property from nation-state and non-state threats.
Charles previously served in the CIA’s Directorate of Operations, conducting and leading intelligence and counterintelligence operations across the Middle East, Europe, and Asia. He also provides training to Fortune 500 companies, U.S. Special Operations Command, the U.S. Intelligence Community, and federal law enforcement.
- Sindhura KonaSecurity Engineer, Confidential
Sindhura is a cybersecurity engineer specializing in emerging threat analysis and enterprise security architecture. With a practitioner's focus on translating complex security research into actionable guidance, Sindhura brings the grounded, real-world perspective to quantum security that is too often absent from discussions dominated by academic theory or vendor messaging. Her presentations are the result of deep research into published attack papers, hardware demonstrations, and the NIST PQC standardization process—distilled into intelligence that IT security teams can act on immediately.
- Steven F. FoxDirector of Information Security & Regulatory Compliance, ETS
Creating value-add business outcomes through security and privacy design is the core of my professional mission. I prioritize understanding my clients’ organizational goals and culture to ensure their infrastructure and processes reflect their ethos. As an IT-to-business translator with extensive technical and business advisory experience, I have successfully led audits testing controls from standards such as NIST CSF, ISO 27001, GDPR, and PCI-DSS. My contributions to the security community include publications in ISSA Journal and CSOonline, and presentations at RSA Conference, Blackhat Executive Summit, and DefCon. As a member of the SecureWorld Expo Advisory Committee, I remain actively engaged in advancing the field of cybersecurity.
- Mike MuscatellSr. Director, Cyber Security, Acumatica, Inc.
Mike Muscatell is a seasoned IT veteran with more than 21 years in the Information Security field. He is a certified ethical hacker (CEH). Was honored as top 100 professionals in the Information Security field by Strathmore's for 2014. Member of a number of security organizations, including InfraGard and the U.S. Chamber of Commerce Cyber Committee.
 Blancco Representative
- Google Cloud Security Representative
 Sublime Representative
- Sumo Logic Placeholder
- Zscaler Representative
- Rhett SaundersExecutive Director of Cybersecurity & Infrastructure, Focus on the Family
Rhett served the Federal Reserve, and while there, led regular Enterprise Risk Management discussions between the Federal Reserve and U.S. Treasury with a focus on cybersecurity. He is a former NSA cryptoanalyst and a U.S. Army veteran, having served multiple joint intelligence communities, both foreign and domestic government agencies in international locations.
Rhett is a public speaker on the topic of privacy and identity theft prevention. He lectures on cybersecurity and cryptography topics at University of Colorado Colorado Springs (UCCS) and Flatiron School. He also serves on the SecureWorld Advisory Council. Rhett earned a Master of Business Administration from LeTourneau University and holds the CISSP credential.
- Col. Cedric LeightonCNN Military Analyst; U.S. Air Force (Ret.); Founder & President, Cedric Leighton Associates, LLC
Cedric Leighton is a CNN Military Analyst and a retired United States Air Force Colonel. On CNN, he has provided incisive commentaries on the Israel-Hamas War, the War in Ukraine, the U.S. withdrawal from Afghanistan, and numerous other conflicts around the world. His analysis has been seen by millions of viewers around the world and provided much needed context to some of the most pressing national security issues of our time. As a U.S. Air Force officer, Colonel Leighton served at U.S. Special Operations Command, the Joint Staff, and the National Security Agency, where he helped train the nation's cyber warriors. A Middle East combat veteran, he is the recipient of numerous military awards, including the Defense Superior Service Medal and the Bronze Star. After serving 26 years as a U.S. Air Force Intelligence Officer, Col. Leighton founded a strategic risk consultancy and became the co-founder of CYFORIX, where he advises multinational businesses on developing better cyber strategies designed to reduce risk and unpredictability.
- VJ ViswanathanFounding Partner, CYFORIX (Former CISO & Sr. Executive at Keurig Dr Pepper, Comcast, HD Supply, and GE)
VJ Viswanathan is a global technology and security executive with more than 25 years of experience spanning AI, cloud and enterprise platforms, cybersecurity, privacy, and technology risk. He has held senior executive roles at large enterprises, including Keurig Dr Pepper, Comcast, HD Supply, and GE, where he led technology, cybersecurity, privacy, and risk programs across highly complex and distributed environments.
Today, VJ works with boards and executive teams on the security challenges created by AI, automation, and digital sprawl—helping leaders understand where traditional security models fall short and how to adapt. He currently serves as Founding Partner of CYFORIX and CEO of TORQE, focused on strategic defense and enterprise transformation.
- Yadi CaroFounder, Hardcore Soft Skills
Yadi Caro is the founder of Hardcore Soft Skills, a company focused on educating teams and individuals on critical skills to prepare for the future of work. She is a Harvard-educated Organizational Psychology practitioner who has been working with teams of developers and engineers for more than 15 years within U.S. military organizations, launching high performing teams and helping organizations to break silos, improve collaboration and innovate. She is the author of Hardcore Soft Skills: A Guide to Work with Humans, host of the Hardcore Soft Skills podcast (listeners in 60+ countries), keynote speaker and team coach. Her online courses are available in multiple platforms, including LinkedIn Learning.
Yadi also holds a Master’s in Communications (Florida International University), and a Bachelors in Philosophy (University of Puerto Rico). Her certifications include Organizational Behavior (Harvard), Project Management Professional (PMP), Certified Agile Coach, Lean Six Sigma, and Business Analytics (MIT). She is also a trained ADHD (Attention Deficit Hyperactivity Disorder) Coach. Yadi is from Puerto Rico, and after living in Miami, and Germany, she now lives in Tampa with her husband and two sons. She is fluent in Spanish, English, proficient in Portuguese and just a little bit of German. Running is her idea generator and traveling is her way to get inspired (32+ countries).
- Micah KimProduct Manager, Datadog
Micah Kim is a Product Manager at Datadog building Observability Pipelines. He works on expanding telemetry processing capabilities to help teams flexibly aggregate, transform, and route data to their preferred destinations. Outside of the office, he loves to ski pow, hike in National Parks, and devour bagels.
Hone your skills and knowledge and earn 6 CPE credits.
