SecureWorld conferences blend world-class keynotes, breakout sessions, small group discussions, and opportunities to earn CPE credits.
 Open Sessions
 Conference Pass
 SecureWorld Plus
 VIP / Exclusive
- Wednesday, December 9, 202610:30 amExhibitor Hall openRegistration Level:
- Open Sessions
10:30 am - 5:00 pmLocation / Room: Exhibitor FloorYour opportunity to visit our solution vendor partners, whose sponsorship makes SecureWorld possible! Peruse the many downloadable resources each booth has to offer.
11:00 amOPENING KEYNOTESponsored by Google CloudRegistration Level:- Open Sessions
11:00 am - 11:45 amSession title and description to come.
11:45 amNetworking BreakRegistration Level:- Open Sessions
11:45 am - 12:00 pmLocation / Room: Exhibitor FloorVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
12:00 pmThe Long Insurgency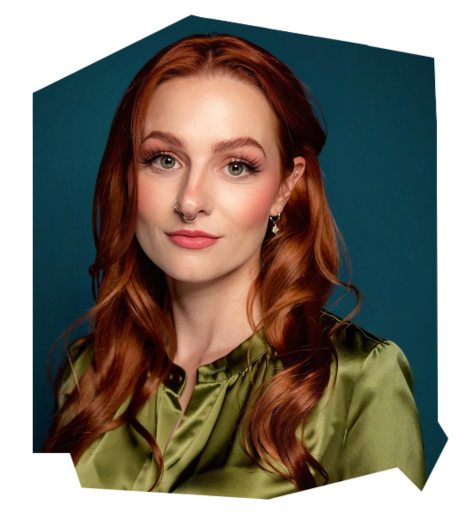 Founder & Principal Advisor, LaMarr LabsRegistration Level:
- Open Sessions
12:00 pm - 12:45 pmThe capability to destroy infrastructure has existed since 2007 and has been rehearsed on Ukraine’s grid with the same vendor products running US plants, yet almost nothing here has been touched. The capability sits idle on purpose because its value lies in being known. An adversary who wants you aware requires different defenses than one who wants you beaten. This is why resilience outperforms deterrence, and the talk closes on what that posture actually looks like for an operator.
12:00 pmThe Global AI Dilemma: How the EU and U.S. Are Balancing Innovation and RegulationRegistration Level:- Open Sessions
12:00 pm - 12:45 pmArtificial Intelligence is impacting our work, and every aspect of our lives, creating both possibilities and challenges. The European Union has enacted broad, mandatory regulations on AI. The United States is focusing on innovation and choosing a different approach by allowing states to decide for themselves. In this session, we explore these two distinct strategies, with a focus on the critical need to balance the protection of human rights and ethical standards, with support for technological advancement.12:00 pmIdentity Security Beyond MFA: Continuous Verification and Risk-Based ControlsRegistration Level:- Open Sessions
12:00 pm - 12:45 pmSession details to come.
12:45 pmNetworking BreakRegistration Level:- Open Sessions
12:45 pm - 1:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
1:00 pmBeyond Login: Designing Identity Controls for Modern Enterprise Products Member of Technical Staff, OpenAIRegistration Level:
- Open Sessions
1:00 pm - 1:45 pmEnterprise identity can no longer be reduced to a login gate. Modern products span admin consoles, workspaces, APIs, and privileged workflows, often across multiple identity providers and assurance levels. This session presents a vendor-neutral architecture that separates principal eligibility, resource authentication requirements, and session assurance. It examines common failures in coarse-grained SSO and shows how teams can introduce stronger controls using policy evaluation, shadow decisions, decision logging, staged enforcement, and rollback safeguards without causing widespread access failures or creating brittle user experiences.
Attendees will leave with a practical architecture and rollout checklist for building resource-aware authentication and authorization controls across complex enterprise products.
1:00 pmCritical Infrastructure Debrief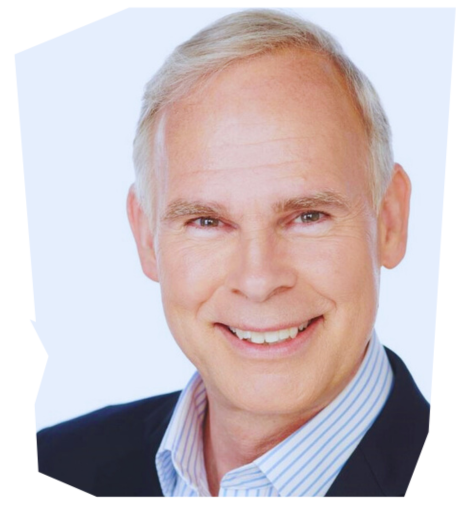 CNN Military Analyst; U.S. Air Force (Ret.); Founder & President, Cedric Leighton Associates, LLC
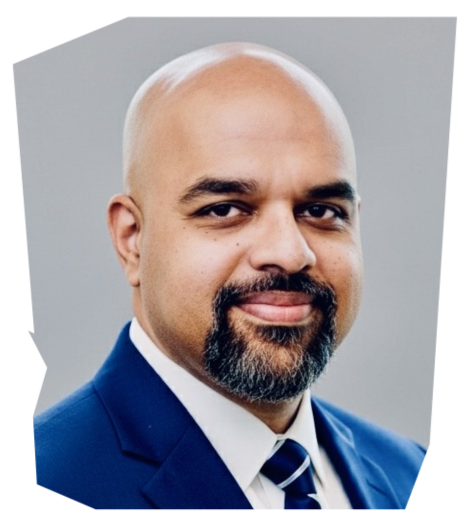 Founding Partner, CYFORIX (Former CISO & Sr. Executive at Keurig Dr Pepper, Comcast, HD Supply, and GE)Registration Level:
- Open Sessions
1:00 pm - 1:45 pmCritical infrastructure is no longer merely a high-value target; it is the front line of modern geopolitical conflict. This session connects the dots between escalating global volatility and immediate risks to cyber-physical systems, operational technology (OT), and public safety. We will examine how nation-state actors and hybrid threat groups are exploiting interdependencies across energy, water, telecommunications, and defense industrial supply chains to execute disruption-first campaigns.
The discussion will pivot to the internal convergence of OT and IT, analyzing the vulnerabilities introduced by edge compute, remote asset telemetry, and the integration of AI-driven industrial automation. From state-sponsored Advanced Persistent Threats (APTs) deploying custom wiper malware against industrial control systems (ICS) to high-extortion ransomware syndicates targeting life-safety environments, we profile the adversaries engineered to disable foundational systems.
Join us for a 2026 outlook that moves beyond standard enterprise compliance, delivering a battle-tested roadmap for cyber-physical resilience, fail-safe architecture, and sovereign asset protection under active operational stress.
1:00 pmBridging the Gap: The Convergence of Cyber and Physical Security in Critical InfrastructureRegistration Level:- Open Sessions
1:00 pm - 1:45 pmAs the digital and physical worlds become increasingly interconnected, the risks to critical infrastructure continue to evolve. In this session, we will explore the convergence of cybersecurity and physical security, highlighting the growing threats that target operational technology (OT) controls and essential systems. Attendees will gain insights into the vulnerabilities that arise when cyber and physical security are not aligned and learn best practices for securing critical infrastructure against emerging threats. Join us for an in-depth discussion on how to mitigate risk and enhance resilience in today’s complex security landscape.
1:45 pmNetworking BreakRegistration Level:- Open Sessions
1:45 pm - 2:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
2:00 pmKEYNOTESponsored Stable SecurityRegistration Level:- Open Sessions
2:00 pm - 2:45 pmSession title and description to come.
2:45 pmNetworking BreakRegistration Level:- Open Sessions
2:45 pm - 3:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
3:00 pmJourney to CMMC LCCA Certification Cyber Third-Party Risk Manager, AbbVieRegistration Level:
- Open Sessions
3:00 pm - 3:45 pmAre you seeking LCCA certification to assess organizations for compliance with the Cybersecurity Maturity Model Certification (CMMC) requirements? Unlike many other cybersecurity certifications, becoming a Lead CMMC Assessor (LCCA) involves specialized qualifications, responsibilities, and requirements. This interactive session will provide an overview of the CMMC assessment ecosystem, including which organizations may be required to obtain CMMC certification and why compliance is essential for protecting sensitive defense-related information. Participants will also learn how Certified CMMC Professionals (CCPs), Certified CMMC Assessors (CCAs), and Lead CMMC Assessors (LCCAs) contribute to the assessment and certification process. We will conclude with an overview of the pathway to becoming an LCCA, including the key steps, expectations, and considerations for professionals interested in pursuing this role.
3:00 pmA Hybrid Approach to Critical Infrastructure Vulnerability Assessment and Governance Founder, Public Value LLCRegistration Level:
- Open Sessions
3:00 pm - 3:45 pmWe can no longer afford to view the critical infrastructure as two (2) separate domains: 1) Physical and 2) Cyber. Today’s critical infrastructure is interconnected, intertwined, and/or fused where an event in one attribute affects the other simultaneously, or in parallel. Therefore, the modern critical infrastructure must be assessed and governed holistically.
The country needs a hybrid vulnerability assessment and governance framework that finds and closes vulnerabilities before America’s adversaries find them.
3:00 pm[Panel] Current Threats to Critical Infrastructure Panel DiscussionRegistration Level:
- Open Sessions
3:00 pm - 3:45 pmCritical infrastructure sectors—from energy grids and water treatment facilities to transportation hubs and healthcare systems—face an unprecedented wave of sophisticated, state-sponsored cyber operations, highly disruptive ransomware, and supply chain intrusions. As traditional operational technology (OT) and industrial control systems (ICS) rapidly converge with hyperscale cloud environments, legacy air-gaps have dissolved, drastically widening the attack surface and introducing severe vulnerabilities across hybrid architectures.
This panel brings together industry leaders to examine the shifting threat landscape targeting essential services and outline modern defense-in-depth strategies. Key areas of focus include:
- Pervasive Network Visibility & Deep Observability: Eliminating blind spots across hybrid IT and OT environments through intelligent traffic monitoring, application metadata extraction, and East-West lateral movement detection.
- Resilient Cloud Infrastructure & Threat Intelligence: Leveraging planetary-scale threat telemetry, zero-trust architectures, and automated cloud-native detection and response to protect centralized management planes and distributed mission-critical workloads.
- Integrated Cyber Protection & Operational Continuity: Unifying endpoint security, AI-powered anti-ransomware defenses, and immutable disaster recovery to guarantee rapid restoration and minimize downtime in the event of an attack.
- OT/ICS Posture Hardening & Attack Surface Management: Implementing rigorous continuous configuration hygiene, micro-segmentation, and proactive risk remediation to safeguard legacy and proprietary industrial field devices.
Attendees will gain actionable insights into how enterprise cloud defenses, deep network telemetry, automated cyber recovery, and industrial system hardening work in concert to build operational resilience against modern cyber threats.
3:45 pmNetworking BreakRegistration Level:- Open Sessions
3:45 pm - 4:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
4:00 pmCLOSING KEYNOTESponsored by AcronisRegistration Level:- Open Sessions
4:00 pm - 4:45 pmSession title and description to come.

 Acronis
 unifies data protection and cybersecurity, delivering cyber protection that solves safety, accessibility, privacy, authenticity, and security (SAPAS) challenges.
Acronis offers antivirus, backup, disaster recovery, endpoint protection management solutions, and award-winning AI-based antimalware and blockchain-based data authentication technologies through service provider and IT professional deployment models. These solutions protect data, applications, and systems in any environment.
 Google Cloud Security
 provides organizations with leading infrastructure, platform capabilities and industry solutions to help them solve their most critical business problems. Google Cloud Security helps customers protect their global operations with solutions such as zero trust security, application and data protection, fraud prevention, and threat detection and response.
 Stable Security
Helping operators understand, secure, and modernize industrial control systems across power, water, and manufacturing.
- Addie LaMarrFounder & Principal Advisor, LaMarr Labs
Addie LaMarr is the founder and principal advisor at LaMarr Labs, a post-quantum cryptography advisory firm. She spent 15 years in cybersecurity, 10 of them securing cryptographic systems inside the US government, in a career that runs from the US Air Force through the Department of Justice. For 8 years in the Air Force she managed encryption systems and cryptographic key material under NSA directives. At DOJ she advised the FBI CISO and the Office of Justice Programs CISO, and contributed to the NIST High Value Asset federal cybersecurity policy project.
- Keyao AnMember of Technical Staff, OpenAI
Keyao An is a Member of Technical Staff at OpenAI, where she builds enterprise identity and access capabilities for complex, large-scale products. Her work focuses on authentication, authorization, multi-IdP SSO, policy-based access control, and the safe deployment of security-critical changes. Previously at Meta, she developed AI-powered business products and safety systems. She specializes in turning complex security and enterprise requirements into resilient product capabilities that balance strong controls, operational reliability, and usable customer experiences.
- Col. Cedric LeightonCNN Military Analyst; U.S. Air Force (Ret.); Founder & President, Cedric Leighton Associates, LLC
Cedric Leighton is a CNN Military Analyst and a retired United States Air Force Colonel. On CNN, he has provided incisive commentaries on the Israel-Hamas War, the War in Ukraine, the U.S. withdrawal from Afghanistan, and numerous other conflicts around the world. His analysis has been seen by millions of viewers around the world and provided much needed context to some of the most pressing national security issues of our time. As a U.S. Air Force officer, Colonel Leighton served at U.S. Special Operations Command, the Joint Staff, and the National Security Agency, where he helped train the nation's cyber warriors. A Middle East combat veteran, he is the recipient of numerous military awards, including the Defense Superior Service Medal and the Bronze Star. After serving 26 years as a U.S. Air Force Intelligence Officer, Col. Leighton founded a strategic risk consultancy and became the co-founder of CYFORIX, where he advises multinational businesses on developing better cyber strategies designed to reduce risk and unpredictability.
- VJ ViswanathanFounding Partner, CYFORIX (Former CISO & Sr. Executive at Keurig Dr Pepper, Comcast, HD Supply, and GE)
VJ Viswanathan is a global technology and security executive with more than 25 years of experience spanning AI, cloud and enterprise platforms, cybersecurity, privacy, and technology risk. He has held senior executive roles at large enterprises, including Keurig Dr Pepper, Comcast, HD Supply, and GE, where he led technology, cybersecurity, privacy, and risk programs across highly complex and distributed environments.
Today, VJ works with boards and executive teams on the security challenges created by AI, automation, and digital sprawl—helping leaders understand where traditional security models fall short and how to adapt. He currently serves as Founding Partner of CYFORIX and CEO of TORQE, focused on strategic defense and enterprise transformation.
- Mary RowleyCyber Third-Party Risk Manager, AbbVie
Mary’s several years of leadership experience encompasses many areas of cybersecurity with a focus on IT risk management, IT audit, security awareness training, vulnerability management and incident response. Her extensive information security background includes working at Henry Ford Health System, Comerica Bank, WorkForce Software, Learning Care Group and Raytheon Technologies, where she built and matured the company’s cyber third-party risk program. She currently serves as Cyber Third-Party Risk Manager at AbbVie. Mary is a graduate from Walsh College with a Master’s degree in Business Information Technology, Information Assurance and holds several certifications including CISSP, CISA and CRISC.
- Leonard CasipleFounder, Public Value LLC
Dr. Leonard Casiple is the founder of Public Value LLC and is a former Green Beret. He is the first in the world to conduct a doctoral study of the CARVER Matrix in a cyber environment. Leonard earned his education from Northeastern University (Doctor of Law and Policy), California Lutheran University (Master of Public Policy and Administration), Thunderbird School of Global Management (Global Master of Business Administration), Excelsior College (BS in Liberal Arts), Defense Language Institute (18-Month Arabic Language Course), JFK Special Warfare Center and School (Special Forces Qualification Course), and Academy of Competitive Intelligence (Master of Competitive Intelligence™).
Hone your skills and knowledge and earn 6 CPE credits.
