SecureWorld conferences blend world-class keynotes, breakout sessions, small group discussions, and opportunities to earn CPE credits.
-
 Member of Technical Staff, OpenAI
-
 Cyber Behavioral Profiler, FBI (Ret.) and Modus Cyberandi
 Open Sessions
 Conference Pass
 SecureWorld Plus
 VIP / Exclusive
- Wednesday, October 21, 202610:30 amExhibitor Hall openRegistration Level:
- Open Sessions
10:30 am - 5:00 pmLocation / Room: Exhibitor HallYour opportunity to visit our solution vendor partners, whose sponsorship makes SecureWorld possible! Peruse the many downloadable resources each booth has to offer.
11:00 amOPENING KEYNOTERegistration Level:- Open Sessions
11:00 am - 11:45 am11:45 amNetworking BreakRegistration Level:- Open Sessions
11:45 am - 12:00 pmLocation / Room: Exhibitor HallVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
12:00 pmBeyond Login: Designing Identity Controls for Modern Enterprise ProductsMember of Technical Staff, OpenAIRegistration Level:- Open Sessions
12:00 pm - 12:45 pmEnterprise identity can no longer be reduced to a login gate. Modern products span admin consoles, workspaces, APIs, and privileged workflows, often across multiple identity providers and assurance levels. This session presents a vendor-neutral architecture that separates principal eligibility, resource authentication requirements, and session assurance. It examines common failures in coarse-grained SSO and shows how teams can introduce stronger controls using policy evaluation, shadow decisions, decision logging, staged enforcement, and rollback safeguards without causing widespread access failures or creating brittle user experiences.
Attendees will leave with a practical architecture and rollout checklist for building resource-aware authentication and authorization controls across complex enterprise products.
12:00 pmRethinking Threat Defense: The Assumptions Behind Modern Security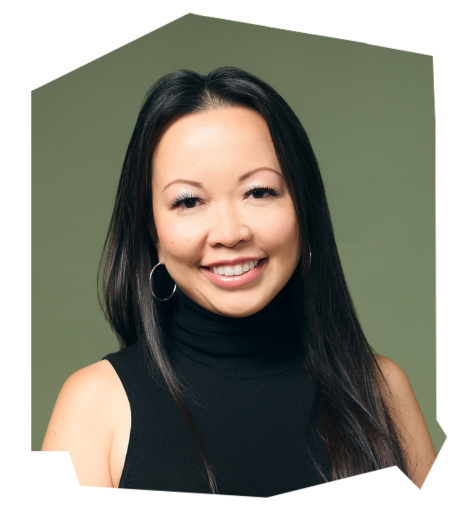 CDO & CDTO | Board Member & Advisor | PodcasterRegistration Level:
- Open Sessions
12:00 pm - 12:45 pmModern security architectures are built on assumptions—about identity, trust, attacker behaviour, analyst workflows, and the boundaries between systems. Those assumptions weren’t mistakes; they were the foundation upon which effective security programs were designed.
As AI reshapes both offensive and defensive capabilities, many of the conditions surrounding those assumptions are beginning to change. The question for security leaders isn’t whether to abandon existing approaches, but how to recognize which assumptions continue to serve us, which deserve to be revisited, and what that means for the future of threat defense.
Rather than focusing on the latest AI tools or attack techniques, this session explores a broader question: how should we think about threat defense when the environment itself is changing? Through the lens of systems thinking, resilience, and organizational adaptation, we’ll examine how AI is influencing the assumptions that underpin modern cybersecurity—and why revisiting those assumptions may become an increasingly important part of building resilient organizations.
12:00 pmDefending the Agentic EnterpriseA Practical Security Model for AI Agents, Identities, and Machine-to-Machine Threats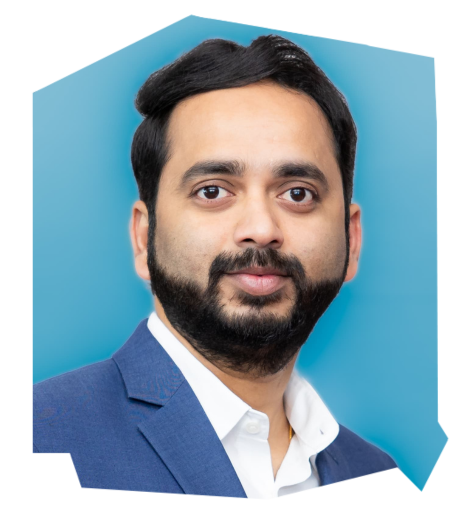 Cloud Solutions Architect, FirstDay FoundationRegistration Level:
- Open Sessions
12:00 pm - 12:45 pmAs AI agents gain access to enterprise applications, APIs, sensitive data, and automated workflows, security teams must defend a new class of autonomous identities. This session presents a practical framework for securing the agentic enterprise by establishing clear human-to-agent-to-tool trust boundaries. It explores least-privilege access, scoped credentials, authorization controls, human approval for high-risk actions, and behavioral monitoring for abnormal agent activity. The session examines how existing Zero Trust, IAM, API security, and cloud security practices can evolve to address agentic threats while enabling responsible AI adoption without creating another isolated security program or adding unnecessary operational complexity.
Attendees will leave with a practical framework to secure AI agents through identity controls, Zero Trust principles, least-privilege access, human oversight, and behavioral monitoring.
12:45 pmNetworking BreakRegistration Level:- Open Sessions
12:45 pm - 1:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
1:00 pmThe AI Intelligence Engine: Governing Every AI Agent Before It Becomes Your Next Insider Threat Chief AI Officer, AngituRegistration Level:
- Open Sessions
1:00 pm - 1:45 pmOrganizations are rapidly adopting AI copilots, autonomous agents, and intelligent workflows, yet most governance models still focus on individual AI systems rather than the enterprise intelligence ecosystem. This session introduces the concept of the AI Intelligence Engine—a centralized governance layer that enables organizations to securely manage AI decision-making, enforce policies, maintain regulatory compliance, and strengthen cybersecurity across all AI-enabled business processes. Attendees will learn a practical framework for governing AI at scale while balancing innovation, operational resilience, and evolving global regulations.
1:00 pmThe Deepfake Kill Chain: How Synthetic Candidates Infiltrate Your Hiring ProcessCyber Behavioral Profiler, FBI (Ret.) and Modus CyberandiRegistration Level:- Open Sessions
1:00 pm - 1:45 pmJust like a cyberattack, a deepfake hiring scam follows a predictable sequence of stages—from reconnaissance and identity fabrication to interview deception and, ultimately, insider access. In this session, we’ll walk through the Deepfake Kill Chain step by step: how bad actors research targets, construct synthetic identities, pass video interviews using real-time face-swapping and voice cloning, and slip past traditional background checks. We’ll examine real-world case studies, break down where each stage can be detected and disrupted, and show how organizations can build defenses at every link in the chain—before a synthetic candidate ever becomes an employee.
1:00 pmFrom Alert Fatigue to Adaptive Defense: Operationalizing AI in the SOCRegistration Level:- Open Sessions
1:00 pm - 1:45 pmSession details to come.
1:45 pmNetworking BreakRegistration Level:- Open Sessions
1:45 pm - 2:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
2:00 pmAI at the Perimeter: How Large-Scale AI Systems Are Reshaping Cybersecurity Risk Sr. Software Development Engineer, AmazonRegistration Level:
- Open Sessions
2:00 pm - 2:45 pmAs organizations race to deploy AI-powered applications, the attack surface is expanding in ways that traditional security frameworks were not designed to handle. This session draws on production engineering experience at Amazon to examine the cybersecurity implications of large-scale AI systems: adversarial inputs, model supply chain risks, inference infrastructure vulnerabilities, and the governance gaps that emerge when AI moves faster than policy. Attendees will leave with a practitioner’s framework for evaluating AI-related risk in their own environments.
2:00 pmAgentic AI, Controlled AutonomyTrust, Compliance, and Override Architecture for Autonomous Enterprise Agents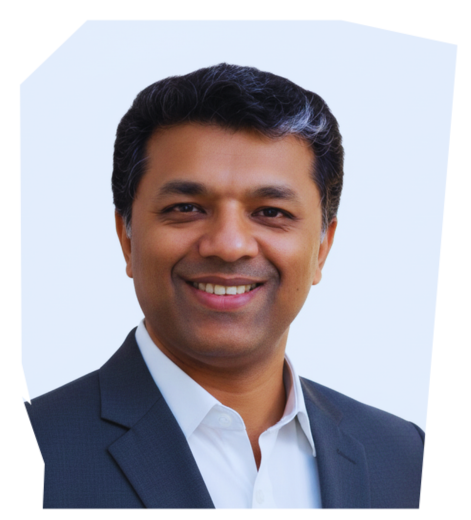 Lead Platform Engineer, Stitch FixRegistration Level:
- Open Sessions
2:00 pm - 2:45 pmAs enterprises push agentic AI into systems that act independently, pricing, discounting, engaging customers, and increasingly making operational decisions across the network itself, the core question shifts from “does the agent work” to “can the enterprise still trust and control it.” This session presents an architectural framework for controlled autonomy: giving agents real decision-making power while keeping enterprise governance, compliance, and security intact.
At the center is a trust layer that scores every AI-generated decision on confidence, policy alignment, and risk, enabling dynamic calibration of human involvement. Low-risk decisions get automated; high-impact ones get escalated, so autonomy scales operationally without giving up governance. Sitting alongside it is compliance-aware orchestration, validating every agent action against dynamic policy graphs in real time, so agents stay within regulatory, contractual, and internal constraints even as multiple agents interact and coordinate.
A major focus is on human override: intelligent escalation triggers and contextual decision summaries that reduce cognitive load and speed up turnaround for security and operations teams managing high-velocity, autonomous environments. We’ll also cover observability, explainability, and auditability, building a transparent decision fabric so every autonomous action stays traceable, a requirement for any security-conscious enterprise deploying agentic systems at scale.
The session closes with enterprise integration patterns, bounded autonomy gateways, and parallel decision simulation, that let organizations deploy agentic AI broadly while keeping governance and security consistent as autonomy expands across the network.
2:00 pmThreat Modeling for Modern Architectures: From Cloud to EdgeRegistration Level:- Open Sessions
2:00 pm - 2:45 pmSession details to come.
2:45 pmNetworking BreakRegistration Level:- Open Sessions
2:45 pm - 3:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
3:00 pmBuy Back Your Time: AI Triage, Real Incidents, a SecOps Case Study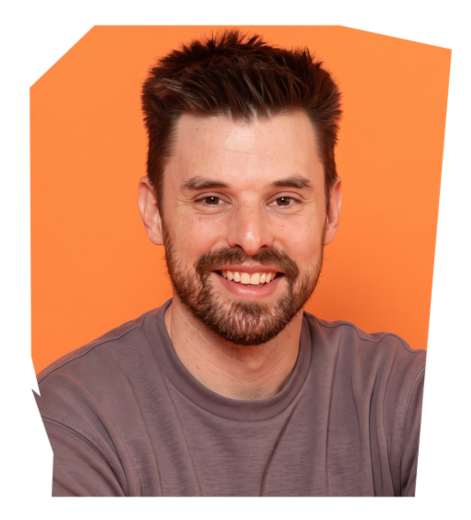 Sr. Manager, Cyber Security & Infrastructure, RoverRegistration Level:
- Open Sessions
3:00 pm - 3:45 pmSecurity operations teams don’t have a headcount problem, they have a signal-to-noise problem. Over the past year, Rover’s ticket volume grew 640%—and our mean time to resolution still went down, at one point dropping four hours in a single month. This talk explains how, and then shows what that time savings actually bought us during a real attack.
First, the mechanics: we built an automated triage pipeline that connects our EDR, SIEM, and phishing tools to an LLM (Gemini). Every alert triggers a purpose-built Lambda that gathers the right context—process trees, sender domain age, login history, the underlying SIEM query—and hands it to the model with a tightly scoped prompt (including explicit instructions to treat email content as untrusted data, not commands). Within seconds, a structured verdict, reasoning, and recommended action lands as a comment on the ticket. Work that took an analyst 20-30 minutes now takes seconds, and every AI verdict is clearly labeled and still requires human sign-off before action.
Then, the case study: this summer Rover faced repeated waves of automated toll fraud—thousands of fake accounts created via disposable email domains to abuse SMS verification across international phone numbers. I’ll walk through how a cross-functional team (fraud ops, engineering, and cybersecurity) used the analyst time freed up by AI triage to focus on the harder problem: real-time network and application-layer countermeasures—domain blocking, feature-flag kill switches, and edge/WAF rules—to contain each wave within hours instead of days. You will leave this presentation with concrete actions you can take back to your organization and ways to implement without a giant budget ask.
3:00 pmSecuring the SaaS Jungle: Access Control and Shadow Data in the CloudRegistration Level:- Open Sessions
3:00 pm - 3:45 pmSession details to come.
3:00 pmThe Developer as a Defender: Integrating Security into CI/CD PipelinesRegistration Level:- Open Sessions
3:00 pm - 3:45 pmSession details to come.
3:45 pmNetworking BreakRegistration Level:- Open Sessions
3:45 pm - 4:00 pmVisit the Networking Hall to network with attendees and connect with our supporting solution providers and association partners.
4:00 pmCLOSING KEYNOTERegistration Level:- Open Sessions
4:00 pm - 4:45 pm

 Doppel
 is the social engineering defense platform using AI to fight AI. Built to outpace and overpower your would-be attackers, our sophisticated AI-forensics see attacks coming and crush them at their source. We safeguard every channel and move faster than attack speed. With intelligence that constantly compounds, we’re perpetually at the forefront of social engineering defenses.
We work relentlessly to defend your brand, people, and future from whatever comes next in social engineering.
 Google Cloud Security
 provides organizations with leading infrastructure, platform capabilities and industry solutions to help them solve their most critical business problems. Google Cloud Security helps customers protect their global operations with solutions such as zero trust security, application and data protection, fraud prevention, and threat detection and response.
 Proofpoint
 protects your people, data, and brand from advanced threats and compliance risks with cybersecurity solutions that work. Built on advanced analytics and a cloud architecture, our platform secures the way your people work today—through email, mobile apps, and social media.
Some attacks get through even the best defenses. That’s why our solutions also proactively safeguard the critical information people create. We reduce your attack surface by managing this data and protecting it as you send, store, and archive it. And when things go wrong, we equip security teams with the right intelligence, insight, and tools to respond quickly.
 Strike48
’s core mission is to help you automate the extraction of business value from server logs. The Strike48 Prospector Studio is an AI Agent Creation and Management Suite that allows you to quickly start inspecting logs with AI agents. Use our Agent creation personas to help create Agents for your purposes or you can use our professionally pre-made Agents instead!
 Zscaler
 is universally recognized as the leader in zero trust. Leveraging the largest security cloud on the planet, Zscaler anticipates, secures, and simplifies the experience of doing business for the world’s most established companies.
- Keyao AnMember of Technical Staff, OpenAI
Keyao An is a Member of Technical Staff at OpenAI, where she builds enterprise identity and access capabilities for complex, large-scale products. Her work focuses on authentication, authorization, multi-IdP SSO, policy-based access control, and the safe deployment of security-critical changes. Previously at Meta, she developed AI-powered business products and safety systems. She specializes in turning complex security and enterprise requirements into resilient product capabilities that balance strong controls, operational reliability, and usable customer experiences.
- Amy YeeCDO & CDTO | Board Member & Advisor | Podcaster
Amy Yee is the Host of the Wired for Change podcast and an executive leader with more than two decades of experience at the intersection of digital transformation, cybersecurity, governance, and technology strategy. Throughout her career, she has held senior executive roles across healthcare, government, and other regulated industries, leading large-scale transformation initiatives and overseeing technology, cybersecurity, privacy, enterprise architecture, and digital strategy.
Today, Amy works with organizations across critical sectors to strengthen cyber resilience while helping leaders navigate the intersection of technology, trust, and organizational change. A frequent international keynote speaker, she is known for blending real-world experience, systems thinking, and compelling storytelling to help audiences think differently about resilience, leadership, and the future of cybersecurity.
- Nisha SirikondaCloud Solutions Architect, FirstDay Foundation
Nishanth Sirikonda is a Cloud and Enterprise Architect and technology leader specializing in cybersecurity, cloud security, enterprise architecture, and secure digital transformation. He leads the architecture and governance of critical enterprise platforms supporting multiple nonprofit organizations, with responsibility spanning identity and access management, security architecture, enterprise applications, integrations, and cloud environments. His work focuses on applying Zero Trust principles, strengthening access controls, managing technology risk, and securely adopting emerging technologies, including AI and intelligent automation.
- Ana Stojkovic KnezevicChief AI Officer, Angitu
Ana Stojkovic Knezevic is Chief AI Officer (CAIO) at Angitu and founder of mAIgla, where she focuses on enterprise AI governance, AI strategy, and intelligent operating models. She advises organizations on building secure, compliant, and scalable AI ecosystems while navigating evolving global regulations. Ana has spoken internationally across North America, Europe, and Asia on AI governance, financial services, and responsible AI. With a background in engineering, project leadership, and enterprise transformation, she specializes in bridging executive strategy, cybersecurity, and practical AI implementation.
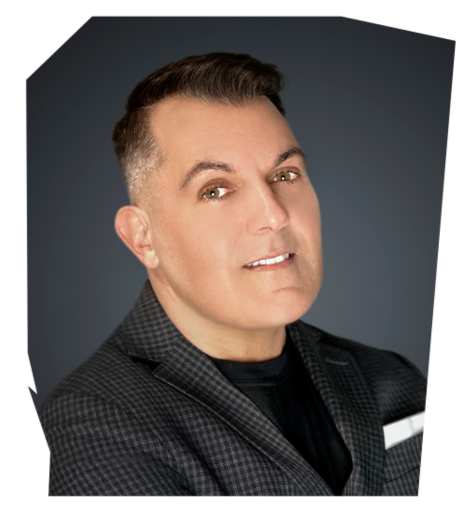
- Cameron H. MalinCyber Behavioral Profiler, FBI (Ret.) and Modus Cyberandi
Cameron Malin, JD, CISSP, is the founder of Modus Cyberandi, a bespoke Cyber Behavioral Profiling consultancy specializing in the assessment of cyber threat actor decision making, adversary tradecraft, cyber deception, and cognitive vulnerabilities. As a retired Behavioral Profiler with the Federal Bureau of Investigation (FBI), he has more than 22 years of experience investigating, analyzing, and profiling cyber adversaries across the spectrum of criminal to national security attacks.
During his tenure in the FBI, he was the founder of both the FBI Behavioral Analysis Unit's (BAU) Cyber Behavioral Analysis Center (CBAC), the FBI BAU's methodology and application of science-based behavioral profiling and assessment to national security and criminal cyber offenders—and the BAU’s Deception and Influence Group (DIG), a uniquely trained and experienced cadre of Behavioral Profilers specialized in analyses and countermeasures to adversary cyber deception campaigns and influence operations.
He is a co-author of the authoritative cyber deception book, "Deception in the Digital Age: Exploiting and Defending Human Targets Through Computer-Mediated Communications" (published by Academic Press, an imprint of Elsevier, Inc.), and co-author of the Malware Forensics book series: "Malware Forensics: Investigating and Analyzing Malicious Code," "Malware Forensics Field Guide for Windows Systems," and "Malware
Forensics Field Guide for Linux Systems" (all published by Syngress, an imprint of Elsevier, Inc.). - Tejas Pravinbhai PatelSr. Software Development Engineer, Amazon
Tejas Pravinbhai Patel is a Senior Software Development Engineer at Amazon and Chair of the Irving ACM Chapter. He holds Fellowship designations from SCRS, BCS, and IET, and has delivered 14+ international keynotes at IEEE and ACM conferences. He has 30+ IEEE Xplore publications in AI systems and inference optimization (h-index 4, 77 citations).
- Surajit PaulLead Platform Engineer, Stitch Fix
- Nick BakerSr. Manager, Cyber Security & Infrastructure, Rover
Hone your skills and knowledge and earn 6 CPE credits.
